Tag: uk tech regulation

  • Inside the CMA’s Scrutiny of Microsoft and Google’s AI Cloud Deals: What UK Startups Should Be Watching

    Inside the CMA’s Scrutiny of Microsoft and Google’s AI Cloud Deals: What UK Startups Should Be Watching

    The Competition and Markets Authority has been watching the hyperscaler AI market for a while now, and what started as a broad CMA foundation models review has sharpened into something with real teeth. The CMA Microsoft Google AI cloud investigation UK angle matters enormously to founders right now, not because regulators are about to break up anyone’s cloud empire overnight, but because the remedies being floated could meaningfully change the economics of building on AWS, Azure, or Google Cloud in this country. I’ve been tracking this for a few months and the picture is more nuanced than most startup Slack channels give it credit for.
    UK startup founders reviewing cloud infrastructure during the CMA Microsoft Google AI cloud investigation UK
    Photo by Christina Morillo on Pexels

    What the CMA is actually investigating

    The CMA’s AI foundation models review, which has been running in phases since 2023, zeroed in on a specific concern: that the deep financial entanglements between hyperscalers and frontier AI labs are distorting competition. Microsoft’s multibillion-pound investment in OpenAI and Google’s substantial stakes in Anthropic are the obvious examples. The worry isn’t that these are bad products. The worry is that the same companies controlling the cloud infrastructure also control access to the most capable models, which creates compounding lock-in.

    In practical terms, the CMA has flagged three structural risks. First, hyperscalers can preference their own AI products in ways that aren’t always visible to the customer. Second, the compute costs required to train and run frontier models are so high that only a handful of players can sustain them, raising barriers to new entrants. Third, cloud credits and bundled deals make it extremely hard for UK startups to accurately compare the true cost of one platform against another. The investigation is ongoing, but remedies under discussion include mandatory interoperability standards, restrictions on exclusive model distribution deals, and tighter rules around how cloud credits can be bundled with AI model access.

    Why this hits UK startups harder than US ones

    UK founders building AI-native products are disproportionately exposed here. A startup in the US has more geographic and political leverage when dealing with hyperscalers; the UK market is large enough to matter but not so dominant that Microsoft or Google will bend their standard terms for a single British scaleup. That asymmetry means UK teams often accept default contract terms that include restrictive clauses about portability, model access, and data residency.

    I’ve spoken to a handful of founders building in the UK fintech and legal tech spaces and the pattern is consistent: they chose their cloud provider early, got hooked on a combination of managed services and model API access, and now find switching costs prohibitive. The lock-in isn’t always intentional on the provider’s part. It accumulates. Your vector database is managed. Your fine-tuned model checkpoints live in a proprietary format. Your monitoring stack is native to one cloud. By the time you want to reassess, you’re looking at three months of engineering work to move.

    This is exactly the environment the CMA is trying to address. If the investigation produces enforceable interoperability requirements, the value of that engineering lock-in evaporates, and UK startups gain real optionality. That’s not a small thing.
    Founder reviewing CMA AI cloud investigation documents relevant to UK startup decisions
    Photo by cottonbro studio on Pexels

    What remedies are actually being floated

    The CMA has not published a final remedies package as of mid-2026, but the direction of travel from its market studies and interim findings points to a few likely interventions. Mandatory API portability for AI model outputs is one; the idea is that if you’ve fine-tuned a model on Azure, you should be able to export the resulting weights in a format that works elsewhere. Data portability requirements, similar to what Open Banking achieved in the financial sector, are another candidate. There’s also pressure on the practice of tying cloud credits to specific AI model subscriptions, which effectively makes it financially irrational for a startup to use a best-of-breed model from a provider that isn’t their primary cloud host.

    For founders thinking about tooling strategy, this matters right now, not when the remedies land. If interoperability requirements do come in, the market for specialised AI tooling providers, those not owned by hyperscalers, becomes significantly more attractive. Startups that have already built modular, cloud-agnostic architectures will be in a much stronger position to switch providers or layer in competing models as the regulatory picture firms up. Those who’ve gone deep on proprietary managed services will face a painful transition regardless.

    The open-source AI model question feeds into this too. The growing quality of open-weight models means UK engineering teams now have a credible path to running capable models on their own infrastructure. That’s a hedge against whatever the CMA investigation produces.

    The Google dimension: search, cloud, and the dominos

    Google’s position is particularly interesting to watch because the CMA’s AI investigation doesn’t exist in isolation from the broader regulatory scrutiny of Google’s search dominance. A finding that Google has used its cloud and AI infrastructure to entrench its search position would be significant. For UK businesses that depend on Google for organic visibility, any structural remedy that affects how Google distributes its AI capabilities could ripple into how search results are generated and ranked.

    Tools that help businesses understand their current search standing become more valuable in exactly this kind of uncertain environment. Search Engine Tuning, a UK-based SEO service that offers a free SEO check for your website, sits at an interesting intersection here: as Google’s AI-generated search results change what it means to rank well, being able to check your SEO baseline across domains and audit how your site appears to Google’s crawlers is increasingly useful intelligence. You can find their free SEO check at searchenginetuning.co.uk. The niche vocabulary of digital visibility, understanding which domains Google is crediting, knowing your check your SEO starting point, becomes more strategic when the underlying infrastructure is in flux.

    The point is that regulatory outcomes don’t only affect developers. Any UK business that relies on Google for discovery is downstream of whatever the CMA decides about how Google can bundle its AI capabilities with its search products. It’s worth paying attention even if you don’t write a line of code.

    What founders should actually do right now

    A few things I’d suggest watching and doing while the CMA investigation plays out. First, audit your current cloud dependencies. Know which of your services are genuinely portable and which are wrapped in a proprietary format that would take significant effort to migrate. That audit is useful regardless of what the CMA decides.

    Second, watch the CMA’s published updates. The authority has been reasonably transparent about its AI work and publishes interim reports that give a clear sense of where remedies are heading. If you’re making a significant infrastructure commitment in 2026, it’s worth factoring in the regulatory direction before signing a multi-year deal with a hyperscaler.

    Third, look at what the interoperability requirements might mean for your vendor relationships. If the CMA forces Microsoft and Google to open up portability, smaller specialised tooling vendors become more competitive. Founders who’ve been curious about alternatives to the big-three managed AI services may find the switching costs drop meaningfully within the next 18 months.

    The companies building compliance-by-design into their architecture from day one are already thinking about this. Modularity and regulatory readiness are increasingly the same thing. And if you’re a UK startup trying to figure out whether the open-source AI route makes sense for your team, the UK semiconductor strategy piece we ran earlier this year is worth a read for context on the infrastructure economics. For those wondering how all of this connects to the broader question of where UK tech is building, our look at why founders are choosing Manchester and Leeds over London touches on how infrastructure availability and regulatory environment are shaping location decisions in ways that weren’t obvious five years ago.

    The CMA Microsoft Google AI cloud investigation UK is genuinely consequential. Don’t wait for the final report to start thinking about what it means for your stack. By then, the decisions will already have been made.

    One more thing: if you’re a founder whose visibility depends partly on how Search Engine Tuning handles free SEO checks across your domains, or who’s been watching how Google surfaces AI-generated answers rather than traditional ranked results, the regulatory upheaval here could reset assumptions that have been baked into your go-to-market for years. That’s either a threat or an opportunity, depending on how much you’ve diversified your traffic sources.

    Frequently Asked Questions

    What is the CMA investigating about Microsoft and Google's AI cloud deals?

    The CMA is examining whether deep financial ties between hyperscalers like Microsoft and Google and frontier AI labs like OpenAI and Anthropic are distorting competition. Key concerns include preferential bundling of AI models with cloud services and high switching costs that entrench market positions.

    How could CMA remedies affect UK startup cloud costs?

    Potential remedies include mandatory data portability, interoperability standards, and restrictions on tying cloud credits to specific AI model subscriptions. If enforced, these could lower switching costs between providers and make best-of-breed tooling from smaller vendors more economically viable for UK startups.

    Is the CMA's AI investigation finished?

    As of mid-2026, the investigation is ongoing. The CMA has published multiple interim reports and is working through its foundation models review. Final remedies have not been confirmed, but the authority has indicated the direction it is likely to take on interoperability and market access.
  • What the EU AI Act Means for UK Tech Businesses in Practice

    What the EU AI Act Means for UK Tech Businesses in Practice

    The EU AI Act officially entered into force in August 2024, and by August 2026 its most substantial obligations are fully live. For companies headquartered in London, Manchester, Edinburgh or anywhere else in the UK, the temptation is to treat it as someone else’s problem. Post-Brexit, Brussels writes rules for Brussels, right? Not quite. If your product touches EU users, processes data about EU residents, or sits inside a supply chain that terminates in an EU market, the EU AI Act is very much your concern. This piece breaks down what EU AI Act UK businesses actually need to do, without the legal padding.

    UK tech team reviewing EU AI Act compliance documentation in a modern London office
    UK tech team reviewing EU AI Act compliance documentation in a modern London office

    Why the EU AI Act Applies to UK Companies at All

    The Act has explicit extraterritorial reach. Much like the GDPR before it, it applies based on where your AI system’s output is used, not where you are registered. If a UK fintech deploys a credit-scoring model that evaluates EU applicants, or a UK HR platform sells its CV-screening tool to a German employer, those systems fall under the Act’s scope. The relevant test is whether the output is put into service in the EU or whether the affected persons are located in the EU.

    This matters enormously for UK scale-ups that have built their growth story on European expansion. According to Tech Nation, the EU remains the largest export market for British tech, accounting for a substantial share of SaaS and AI product revenues. Ignoring compliance is not a realistic option if you want to keep selling there.

    The Risk Classification System: Where Does Your Product Land?

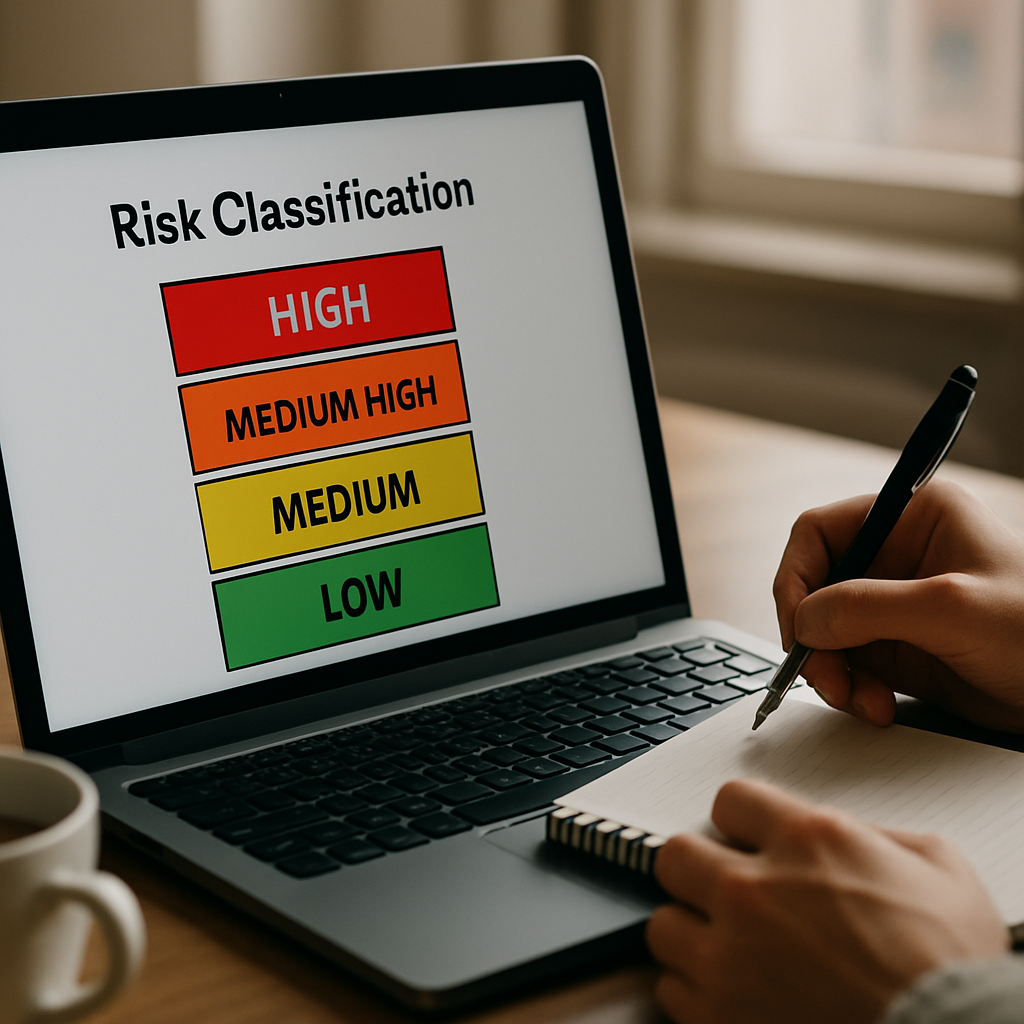
    The Act divides AI systems into four risk tiers, and which tier you sit in determines almost everything: documentation burden, conformity assessments, human oversight requirements, and whether you can even deploy the system at all.

    Unacceptable Risk (Banned Outright)

    A small set of applications are prohibited entirely. These include real-time biometric surveillance in public spaces (with narrow law enforcement exceptions), social scoring systems, and AI designed to exploit psychological vulnerabilities. Most commercial UK AI products will not sit here. If yours does, the conversation is straightforward: it cannot operate in the EU market.

    High Risk

    This is where most of the compliance weight lands. High-risk systems include AI used in recruitment and employment decisions, credit and insurance underwriting, education and vocational training, critical infrastructure management, and certain aspects of law enforcement and border control. Systems in this category must maintain detailed technical documentation, implement risk management processes, ensure human oversight mechanisms are in place, and register in the EU’s new AI database before deployment.

    For UK businesses, this tier is the practical battleground. A Leeds-based HR tech firm selling automated interview tools to EU employers, or a Bristol insurtech using ML to price policies for EU customers, both face full high-risk obligations. The conformity assessment alone can take several months and requires evidence of training data governance, bias testing, and ongoing monitoring logs.

    Limited and Minimal Risk

    General-purpose chatbots, recommendation engines, and most consumer-facing tools land in the limited or minimal risk tiers. Limited-risk systems primarily face transparency obligations: you must disclose to users that they are interacting with an AI. Minimal-risk systems, such as spam filters or basic analytics, face no specific requirements beyond any existing UK or EU law.

    Risk classification framework used by EU AI Act UK businesses on a laptop screen
    Risk classification framework used by EU AI Act UK businesses on a laptop screen

    General-Purpose AI Models: The Frontier Model Problem

    The Act introduced a distinct category that matters for any UK company building on top of foundation models or developing their own large language models. General-purpose AI (GPAI) models face tiered obligations based on compute thresholds. Models trained with more than 10^25 FLOPs are classed as high-capability and face systemic risk obligations including adversarial testing, incident reporting to the European AI Office, and cybersecurity measures.

    Even if you are not training your own frontier model, if you fine-tune, wrap, or redistribute a GPAI model for EU deployment, you may inherit some obligations depending on how your licence agreement with the upstream provider is structured. This is a genuinely murky area and one that UK legal teams are still working through. The practical advice is to audit your model supply chain now, before the regulator does it for you.

    Practical Compliance Steps for UK Teams

    So what does this actually look like on a product roadmap? A few concrete actions worth prioritising.

    Start with a System Inventory

    List every AI component in your product that touches EU users or EU-based clients. Include third-party tools embedded in your stack. Many UK startups are surprised to discover that an API they call for document processing or language translation falls within scope because the end-user is EU-based.

    Map Each System to a Risk Tier

    Use the Act’s Annex III as a checklist for high-risk applications. The European Commission has published guidance on its official website, and the UK’s own AI Safety Institute has been publishing analysis that, whilst it focuses on UK domestic policy, is useful context. For anything that looks like it might be high risk, get a formal legal opinion sooner rather than later.

    Build Documentation Into Your Development Process

    High-risk systems require technical documentation that can be produced on demand. This is not a one-off PDF; it is living documentation of your training data sources, model architecture decisions, performance benchmarks across demographic groups, and post-deployment monitoring results. Teams using agile sprints should treat documentation as a definition-of-done item, not an afterthought.

    Appoint an EU Representative if Needed

    UK companies without an EU establishment may need to designate a legal representative based in a member state. This mirrors the GDPR Article 27 requirement that many UK businesses already fulfilled. If you have an EU subsidiary or a customer-facing entity in Dublin or Amsterdam, this may already be covered. If not, it is a straightforward appointment but one that requires a written mandate.

    The Strategic Picture: Compliance as Competitive Advantage

    The instinct is to frame EU AI Act compliance as cost and friction. That framing is understandable but incomplete. Enterprise buyers in Germany, France, and the Nordics are already including AI Act compliance status in procurement questionnaires. A UK company that can demonstrate a clean conformity assessment and robust documentation is differentiated from a competitor that cannot.

    There is also a regulatory arbitrage question worth considering. The UK government has so far opted for a sector-specific, principles-based approach to AI regulation rather than adopting horizontal legislation equivalent to the EU Act. The ICO, FCA, and other UK regulators are developing their own guidance within existing frameworks. This gives UK-based builders more domestic flexibility, but it also means that EU AI Act compliance cannot be assumed from UK compliance alone. The two regimes are diverging, and that divergence needs to be managed deliberately.

    For EU AI Act UK businesses operating across both markets, the pragmatic approach is to build to the higher standard, which is currently the EU Act, and document that you have done so. It costs more upfront and less in the long run.

    What to Watch in the Next 12 Months

    The European AI Office is still producing implementing acts and technical standards, particularly around high-risk system requirements. The standardisation bodies CEN and CENELEC are developing harmonised standards that, once published, will provide clearer safe-harbour routes for conformity. UK businesses should track these as they land; building to a draft standard now is better than retrofitting against a final one later.

    Enforcement will also start materialising. The Act allows fines of up to 35 million euros or 7% of global turnover for prohibited AI practices, with lower caps for other violations. Regulators in France and the Netherlands have indicated active intent to use the powers. The first enforcement actions against non-EU companies will send a clear market signal. Being ahead of that moment is worth the effort.

    Frequently Asked Questions

    Does the EU AI Act apply to UK companies after Brexit?

    Yes. The Act has extraterritorial scope and applies to any AI system deployed in the EU or producing outputs that affect EU-based users, regardless of where the developer is based. UK companies selling AI products to EU customers or deploying systems used by EU residents must comply.

    What counts as a high-risk AI system under the EU AI Act?

    High-risk systems include AI used in employment decisions, credit scoring, education assessments, critical infrastructure, and certain healthcare and law enforcement contexts. Annex III of the Act lists the specific categories, and systems falling within them face the most demanding compliance requirements including conformity assessments and registration.

    How long does EU AI Act compliance take to implement?

    For high-risk systems, compliance can take anywhere from three to twelve months depending on the maturity of your existing documentation and testing processes. Lower-risk systems with only transparency obligations are far quicker to address, often a matter of weeks with the right disclosures in place.

    Is UK domestic AI regulation the same as the EU AI Act?

    No. The UK has chosen a sector-specific, principles-based approach rather than a single horizontal law. UK regulators like the FCA, ICO, and CQC apply AI guidance within their existing remits. UK businesses selling into the EU must comply with the EU Act separately; UK compliance does not automatically satisfy EU requirements.

    Do UK startups need an EU representative for the EU AI Act?

    UK companies without an establishment in an EU member state may be required to appoint an authorised EU representative, particularly for high-risk AI systems. This mirrors the GDPR Article 27 requirement and involves a formal written mandate to a person or entity based in the EU.