Author: Ethan Miller

  • Why UK B2B Founders Are Choosing Manchester and Leeds Over London for Their Company HQ

    Why UK B2B Founders Are Choosing Manchester and Leeds Over London for Their Company HQ

    Something has been quietly shifting in where UK B2B tech companies choose to plant their flag. Not a dramatic overnight exodus, but a measurable, structural drift that shows up clearly when you pull Companies House registration data by geography and cross-reference it with the kinds of businesses being formed. Manchester and Leeds are no longer just regional also-rans in the UK startup conversation. For a growing cohort of B2B tech founders, they’re the first choice, not the fallback.
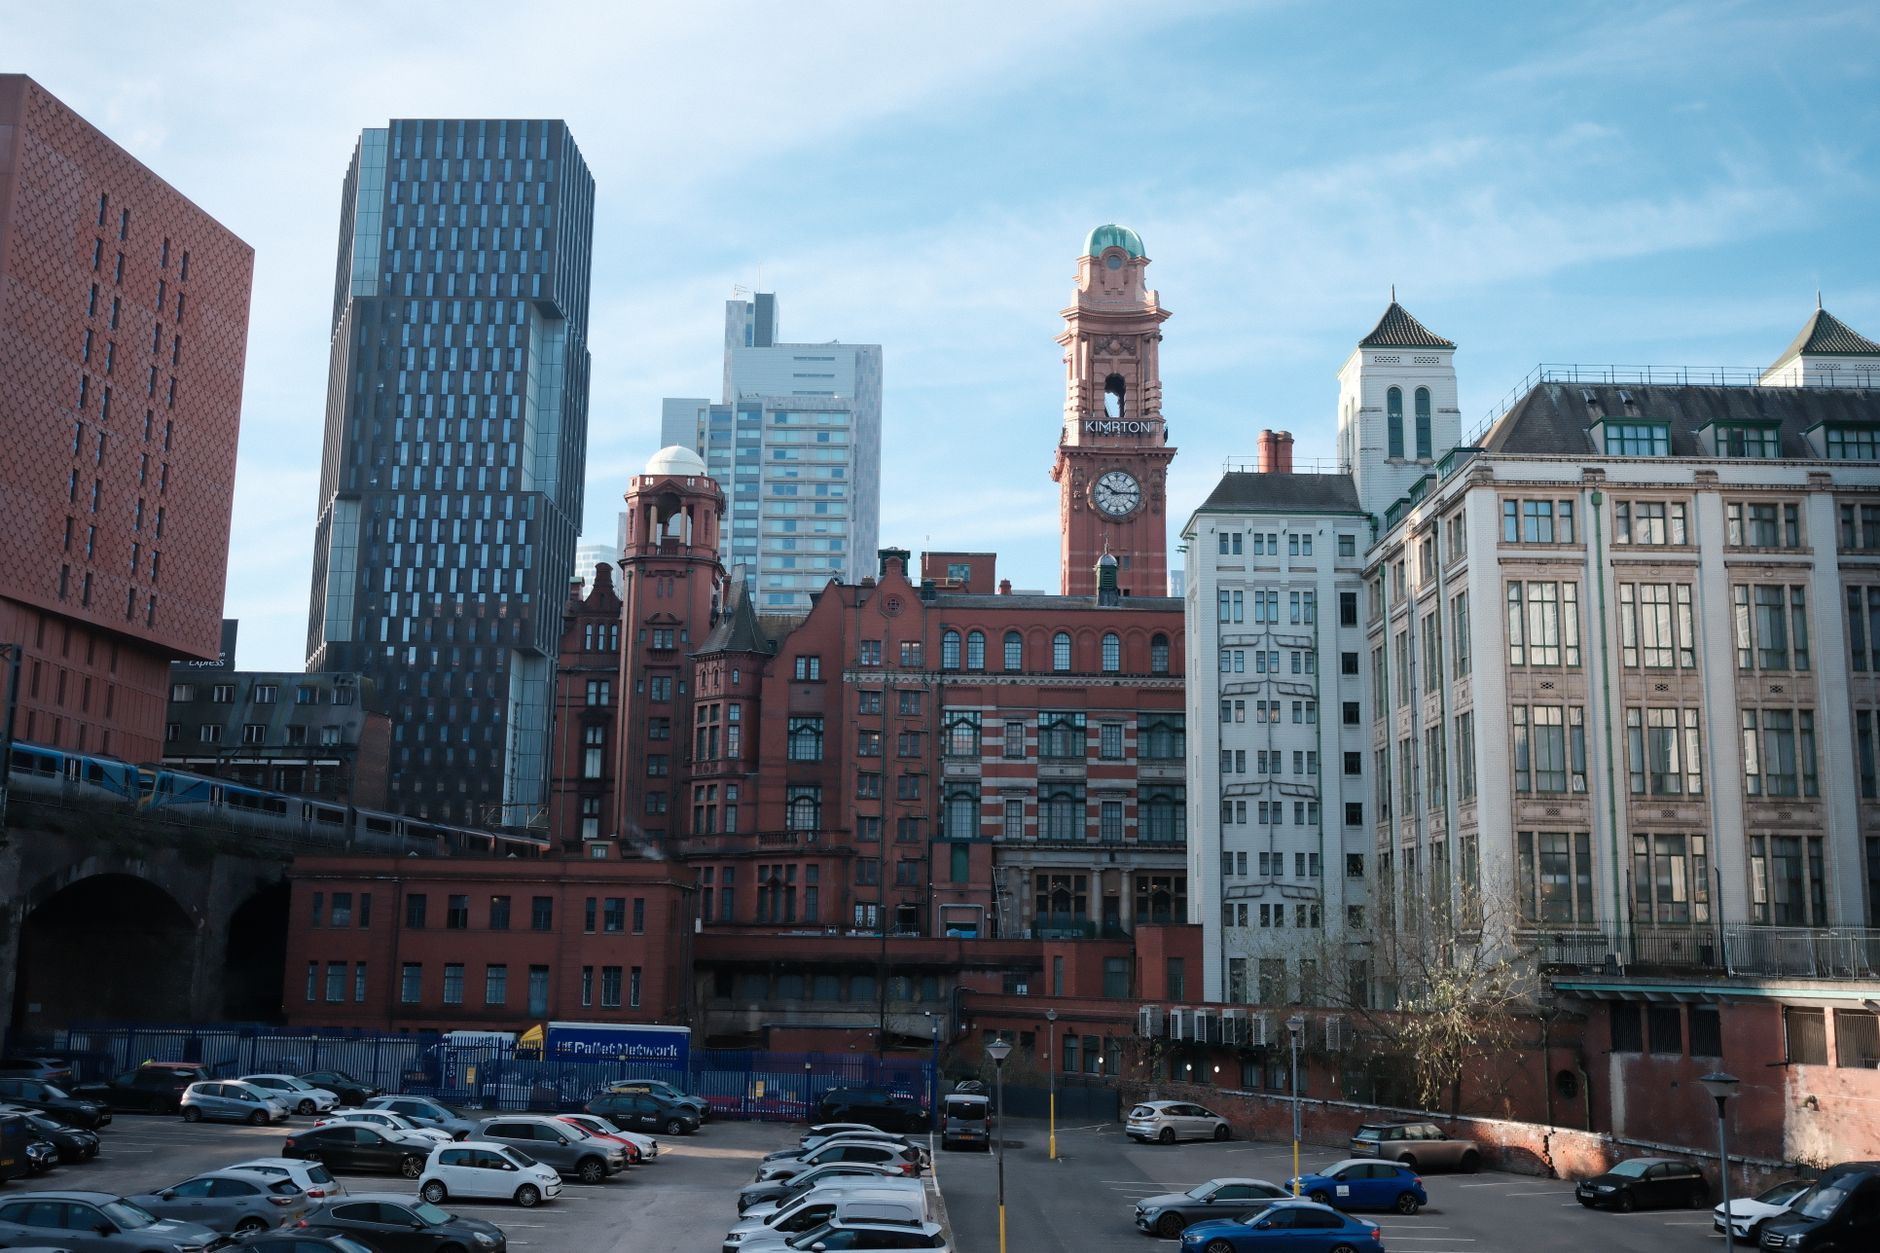
    Modern office buildings in central Manchester representing the UK tech startup HQ Manchester Leeds vs London trend
    Photo by Max W on Pexels

    I’ve spoken to founders who’ve made this call deliberately, and their reasoning is consistent enough to be worth mapping properly. This isn’t about London being bad. It’s about the specific maths of running a B2B software business, where your cost base, your talent pipeline, and your customer relationships all interact in ways that make the northern cities increasingly rational choices. The question worth asking is: what changed, and is it permanent?

    What the Companies House data actually shows

    According to ONS business demography figures, the proportion of new enterprise registrations occurring outside London has been rising steadily since 2020. More specifically, the Leeds City Region and Greater Manchester both recorded above-average growth in professional and technical services registrations between 2022 and 2024, the most recent full-year data available. That category includes the SaaS, data infrastructure, and B2B platform businesses that define the current generation of UK tech.

    Companies House records bear this out at a more granular level. Search for recently incorporated limited companies in the SIC codes associated with software development, data processing, and IT consultancy, and filter for registered offices in M1 to M4 or LS1 to LS11 postcodes, and the volume is striking. This isn’t just one-person consultancies registering a convenience address. Many of these are seed-funded businesses with real headcount, genuine revenue ambitions, and institutional backing.

    The office cost argument is real but it’s not the whole story

    The obvious starting point is cost. Grade A office space in central Manchester runs at roughly £35 to £40 per square foot per year. In the City of London or Shoreditch, comparable space sits at £65 to £85. For a 20-person B2B tech company that wants a proper office rather than hot-desks in a WeWork, that difference compounds fast. But I’d argue founders who’ve relocated or incorporated in the North aren’t primarily driven by rent savings. The rent saving is the bonus, not the thesis.

    The real driver is the talent market. Manchester and Leeds have both developed genuinely deep technical talent pools over the past decade, partly because local universities (Manchester, Leeds, Sheffield, York) have strong computer science and data science departments, and partly because enough companies have now set up there that engineers have career optionality without moving south. When engineers have optionality, they stop treating northern roles as stepping stones. That changes the hiring dynamic entirely.

    This connects to something I’ve watched play out with salary benchmarking in the AI era. London salaries for senior engineers have been inflated by Big Tech presence and a decade of VC-funded bidding wars. Manchester and Leeds haven’t seen the same inflation. A principal engineer in Manchester might be on £80,000 to £95,000 where the same role in London commands £110,000 to £130,000. For a B2B SaaS company that needs to keep burn low through to Series A, that differential is material.

    What B2B specifically means for this calculation

    Consumer tech companies benefit from being in London partly because the press, the influencer ecosystem, and the consumer attention are all concentrated there. B2B is different. Your customers are procurement leads, CTOs, and operations directors sitting in offices across the country. A Manchester or Leeds address is not a credibility handicap in a procurement conversation with a Yorkshire manufacturing firm, a Birmingham logistics company, or a Scottish NHS trust. If anything, it can be an advantage, a signal that you understand the real commercial landscape outside the M25.

    Several of the founders I’ve spoken to made the point that their actual sales process happens on video calls, at trade shows in Birmingham or Manchester itself, and through referrals. The geography of closing enterprise software deals in the UK is not London-centric in the way it was a decade ago. The pandemic accelerated that, and it hasn’t reversed.

    Investor presence has caught up, though the gap hasn’t fully closed

    The honest caveat is that investor geography still skews south. The majority of UK venture capital by value is deployed from London-based funds. But the picture is more nuanced than that headline suggests. Firms like Praetura Ventures in Manchester, Mercia Asset Management with its Northern coverage, and the British Business Bank’s regional funds have all become more active. The North West and Yorkshire combined attracted over £500 million in venture investment in 2023, according to Beauhurst’s regional data, a number that would have seemed implausible five years earlier.

    Founders raising seed or pre-seed rounds increasingly tell me that their lead investor didn’t care about HQ location at all, especially if the founding team had London-adjacent credentials or could demonstrate a remote-friendly culture. Series A and beyond gets more complicated, but by that stage a company operating profitably out of Leeds or Manchester has something more compelling than a postcode to put in front of a London fund.

    Quality of life as a legitimate business variable

    I’ll be direct about something that gets talked around in polite business coverage: quality of life affects founder retention and co-founder relationships in ways that show up in company outcomes. A first-time founder burning through savings whilst paying London rent, commuting on the Jubilee line, and trying to recruit engineers is under a specific kind of pressure that compounds every decision. The same person running a lean operation in a flat in Chorlton or Headingley, cycling to the office, and buying a round of pints for the team on a Friday without wincing, is making decisions from a different baseline.

    This is not a soft argument. Founder mental state is a hard variable in early-stage company survival. The data on startup failure rates in the first three years is grim enough without adding avoidable financial pressure to the stack.

    The structural shift is also happening in adjacent professional services. The rise of UK legal tech has produced specialist startup law firms with genuine Northern presence, making incorporation and early-stage legal work easier to handle locally. The ecosystem services that used to require a trip to EC1 are increasingly available without it.

    This trend is about more than geography

    The question I keep returning to is whether this is a cyclical blip tied to post-pandemic remote working sentiment, or a structural change in where UK tech builds its foundations. My reading of the data is that it’s structural, driven by compounding effects: talent pools that are now self-sustaining, investor networks that have genuinely developed, and a generation of founders who grew up outside London and don’t carry the assumption that the capital is the only valid place to build something serious.

    For founders still weighing the decision, the honest answer is that neither Manchester nor Leeds is right for every B2B business. If your customers are exclusively London financial services firms and your entire leadership network is in Soho, the calculus changes. But if you’re building infrastructure, logistics software, HR tech, procurement tooling, or any of the other categories where your customers are distributed across the UK, the argument for incorporating in the North is now genuinely strong, and the friction of doing so has largely disappeared.

    The UK tech startup HQ Manchester Leeds vs London debate used to be about aspiration versus pragmatism. Increasingly, for B2B founders who’ve run the numbers, it’s just the rational call. And there’s something worth noting in the fact that the founders making it aren’t doing so reluctantly.

    Frequently Asked Questions

    Is it harder to raise VC funding if my startup is based in Manchester or Leeds rather than London?

    It can be slightly harder at Series A and beyond, where most large UK funds are London-based, but the gap has narrowed significantly. Seed-stage funding is now genuinely accessible from Northern-focused investors like Praetura Ventures and Mercia, and many London funds will back strong teams regardless of postcode.

    How do I find technical talent for a B2B tech startup in Manchester or Leeds?

    Both cities have deep pipelines from universities including Manchester, Leeds, and Sheffield, as well as established tech communities built around companies like AutoTrader, Sky Betting and Gaming, and Moneysupermarket. Hiring at senior level is competitive but salaries are materially lower than London equivalents, which helps extend runway.

    What are the actual cost differences between running a tech company in Manchester versus London?

    Grade A office space in central Manchester costs roughly £35 to £40 per square foot annually, compared to £65 to £85 in central London. Senior engineering salaries in Manchester typically run £25,000 to £35,000 lower per head than London equivalents, which compounds significantly across a team of 20 or more.
  • The B2B LinkedIn Creator Playbook UK Tech Founders Are Actually Using to Win Clients in 2026

    The B2B LinkedIn Creator Playbook UK Tech Founders Are Actually Using to Win Clients in 2026

    There is a specific type of LinkedIn post I keep seeing from British SaaS founders right now. It is not a product announcement. It is not a thought leadership essay about digital transformation. It is a brutally honest breakdown of one mistake they made in their sales cycle, what it cost them in MRR, and exactly what they changed. Thirty to forty lines, no fluff, posted on a Tuesday morning. And it is generating qualified demo requests at a rate that paid LinkedIn ads simply cannot match.

    The shift in how UK B2B SaaS startups are winning clients has quietly accelerated over the past eighteen months. Founders who used to rely on cold email sequences, SDR teams, and conference networking are now treating LinkedIn as a primary commercial channel, not a vanity channel. This is the LinkedIn B2B content strategy UK founders are actually building, not the sanitised version the platform’s own marketing team would have you believe.

    UK tech founder writing a LinkedIn B2B content strategy post at a modern desk
    Photo by William Fortunato on Pexels

    Why LinkedIn works differently for B2B technical founders

    LinkedIn’s algorithm heavily favours personal profiles over company pages. I have seen this first-hand across several founders I know: a post from the person who built the product routinely outperforms the same content posted from the company account by a factor of five to ten in raw reach. The platform rewards authenticity signals, comments, saves, shares from relevant networks, and a founder talking about a genuine operational problem gets those signals in a way that brand content rarely does.

    The mechanism matters here. UK B2B buyers, particularly in financial services, legal tech, and logistics, are increasingly doing pre-qualification research on LinkedIn before they ever engage with a vendor’s website. According to the UK government’s digital strategy framework, professional digital engagement is central to how procurement decisions now form at SME level. When a CFO or Head of Operations at a 200-person professional services firm spots a founder consistently writing about problems they recognise from their own operations, the inbound enquiry that follows is already 60 to 70 per cent of the way through a qualification process before the first call happens.

    Content formats that are actually generating pipeline

    I have spoken to a handful of UK founders and consultants who are seeing measurable commercial returns, and the formats breaking through in 2026 are not what the LinkedIn influencer industrial complex tends to promote.

    Failure dissections. A 35-line post structured as: what we did, what went wrong, the specific cost (in revenue, time, or credibility), what we changed. Founders at firms like Clay users in the UK RevOps space report that these posts generate more qualified DMs than any success story they have ever posted. Buyers trust people who can diagnose problems, because problem diagnosis is what they are paying for.

    Process teardowns with specific numbers. Not “we improved our onboarding” but “we cut our time-to-first-value from 23 days to 9 days by removing three onboarding calls and replacing them with one Loom video series, here is the exact sequence and why each call was actually costing us retention.” The specificity is what earns shares from people who then tag colleagues.

    Short-form video, but narrowly scoped. Two to three minutes, recorded on a decent webcam, covering one very specific technical or commercial decision. Not a product demo. Not a brand film. Founders who are running engineering-led companies tend to do well here because they can talk in the language of their buyers’ technical teams, which fast-tracks trust.

    Contrarian positions on industry orthodoxy. The format is: “The [widely accepted practice] is making your [metric] worse, here is why.” UK technical founders have an advantage here because the British instinct to be slightly sceptical and dry in delivery reads very naturally in this format. It generates argument, which generates reach, which generates awareness from exactly the audience you want.

    Posting cadence: what the data from serious practitioners looks like

    The founders I have observed getting consistent pipeline from LinkedIn are posting three to four times per week. Not daily. Not once a fortnight. Three to four posts, with Tuesday through Thursday as the primary publishing window for maximum professional-hours visibility in UK time zones (GMT/BST).

    More important than frequency is consistency of topic cluster. The founders generating inbound are not posting about everything they find interesting. They are known for a specific intersection, warehouse automation and unit economics, or legal tech and regulatory compliance, or fintech architecture and FCA obligations. This is the difference between a personal brand and a personal broadcast channel. If I look at someone’s last ten posts and can describe their positioning in one sentence, that is someone who is building pipeline. If those ten posts cover five different topics, they are not.

    The comment strategy matters as much as the posting strategy. Spending twenty to thirty minutes per day leaving genuinely substantive comments on posts from people in your ICP (ideal customer profile) is, by every founder account I have heard, worth at least as much as one original post per week. You are appearing in the notifications of exactly the right people, you are demonstrating expertise in context, and you are not asking for anything. This is how relationships that convert into pipeline actually start on the platform.

    Measuring what actually matters

    LinkedIn’s own analytics are not particularly useful for this kind of activity. Impressions and follower counts are noise. The metrics that serious practitioners track are: inbound DMs per month from ICP-fit profiles, percentage of those that convert to a discovery call, and the close rate on deals where LinkedIn was the first touchpoint versus outbound-sourced deals.

    One pattern I keep hearing is that LinkedIn-sourced deals close faster and at higher average contract values. The hypothesis is straightforward: someone who has been consuming your content for six to twelve weeks before making contact has already done much of their own qualification. They know your positioning, your thinking, your pricing philosophy, and your flaws (because you wrote about them). The first call is not about establishing credibility, it already exists. It is about scoping the engagement.

    This connects to a broader point about how UK tech firms are rethinking the commercial value of expertise in their teams. The founders generating the best LinkedIn results are not necessarily the most prolific writers. They are the people whose operational knowledge is genuinely specific enough that articulating it creates a differentiation signal. A generalist posting generalist content is invisible. A founder who has spent three years solving one problem for one type of buyer, and can write about it with that specificity, is findable by the exact people who need that problem solved.

    What separates serious practitioners from noise

    There is a lot of LinkedIn content from UK tech founders that looks like pipeline generation but is not. The tell is that it is written for peers, not for buyers. Posts that perform well in terms of likes from other founders, other marketers, other startup people, but generate zero inbound from actual decision-makers at prospective clients. It feels good. It does not pay the bills.

    The founders who have cracked this write with their buyer in their head, not their peer group. They are thinking: what does a Head of Operations at a 150-person logistics firm need to understand about this problem to recognise that they have it? That discipline is genuinely hard to maintain, especially when peer validation is immediately rewarding and buyer validation arrives on a much longer delay.

    The other separator is patience. The founders I know who are getting five to eight qualified inbound leads per month from LinkedIn alone have been posting consistently for nine months to a year. There is no shortcut. The compounding effect is real but slow. Anyone selling a thirty-day LinkedIn growth programme is selling something else entirely.

    For UK founders who are also thinking about how their broader go-to-market model is evolving, LinkedIn content is not a replacement for a structured sales function. It is a lead quality filter. The pipeline it generates tends to be better qualified than outbound. Getting that balance right is a different conversation, but one worth having before you hire your next SDR.

    Frequently Asked Questions

    How often should UK B2B founders post on LinkedIn to generate inbound leads?

    Three to four times per week is the posting cadence most consistently reported by UK founders seeing genuine pipeline results. Consistency and topic focus matter more than raw frequency, posting daily about five different subjects is far less effective than posting three times weekly about one specific problem you solve.

    What types of LinkedIn content work best for B2B SaaS founders in the UK?

    Failure dissections with specific numbers, process teardowns with measurable outcomes, and contrarian positions on industry orthodoxy consistently outperform product announcements and generic thought leadership. The specificity of the numbers and the operational detail is what earns trust with technical buyers.

    How long does it take to see pipeline results from a LinkedIn content strategy?

    Most serious practitioners report that meaningful inbound pipeline from LinkedIn takes nine months to a year of consistent posting to materialise. The compounding nature of personal brand-building on the platform means early results are slow, but deals sourced via LinkedIn typically close faster and at higher values once the flywheel starts.

    Should UK founders post from their personal profile or their company page?

    Personal profiles significantly outperform company pages on LinkedIn for reach and engagement, often by a factor of five to ten on equivalent content. The platform’s algorithm rewards authentic individual voices, so founders should be the primary content creators rather than relying on brand accounts.

  • Inside the ICO’s AI Audits: What UK Businesses Are Actually Being Asked to Prove

    Inside the ICO’s AI Audits: What UK Businesses Are Actually Being Asked to Prove

    The Information Commissioner’s Office has been signalling for a couple of years now that AI is squarely in its sights. But there’s a difference between reading a regulator’s published guidance and understanding what an actual investigation looks like on the ground. ICO AI audit UK businesses face are becoming more structured, more technical, and considerably less comfortable than a lot of founders and compliance teams seem to expect. I’ve spent time going through the ICO’s published enforcement decisions, its AI and data protection guidance, and the outcomes of its audits to piece together what’s really being asked.

    Professional reviewing ICO AI audit compliance documentation in a UK office
    Photo by Kampus Production on Pexels

    What the ICO is actually looking for

    The ICO’s starting point with any AI product is always the same: where does the data come from, and on what legal basis was it used? This sounds simple. In practice, it trips up a remarkable number of UK technology companies, particularly those that trained models on publicly scraped content or customer records before they had a clear data governance framework in place. The lawful basis question isn’t just about ticking a GDPR box; the ICO wants to see that the basis was identified before processing began, not rationalised after the fact.

    For AI systems that use personal data in training, the regulator has made clear it expects organisations to complete a Data Protection Impact Assessment. This is a formal document, not a paragraph buried in a slide deck. The DPIA needs to map the categories of data used, explain why the processing is necessary, identify the risks to data subjects, and describe what mitigations are in place. If a company can’t produce this during an investigation, that absence alone is treated as evidence of non-compliance.

    Automated decision-making: the part most teams get wrong

    Article 22 of UK GDPR is where a lot of AI products run into serious difficulty. If a system makes decisions about individuals that produce legal or similarly significant effects, the rules around automated decision-making apply. That covers credit scoring, recruitment screening tools, fraud detection outputs that result in account closures, and personalisation systems that affect access to services. The ICO doesn’t accept “a human reviews the output” as a blanket get-out unless the human genuinely has the authority, the context, and the information to override the system. Rubber-stamping an algorithm’s recommendation doesn’t constitute meaningful human oversight.

    Real enforcement cases illustrate this clearly. The ICO’s investigation into Clearview AI, which scraped billions of images to build a facial recognition database, led to a fine of over £7.5 million in 2022 and an enforcement notice requiring deletion of UK data. The lawful basis for collecting that data simply did not exist. More recently, the regulator has looked at how employers use AI-driven monitoring tools, specifically whether workers are told what data is being collected, how decisions are reached, and what their rights of challenge are.

    ICO AI audit UK businesses compliance documents and data governance records on a desk
    Photo by Mikhail Nilov on Pexels

    The transparency test

    Transparency is probably the area where I see the biggest gap between what companies think they’re doing and what the ICO actually expects. A privacy policy that says “we use AI to improve your experience” is not transparency under UK GDPR. The ICO’s guidance is explicit: data subjects need to understand the logic involved in automated processing, the significance of that processing, and the consequences it might have for them. This has to be communicated in plain English, not buried in a legal annex.

    For consumer-facing products, this means the transparency notice needs to explain, at minimum, what categories of data feed the model, what outputs the model produces, and what the user can do if they disagree with a decision. For B2B tools where the deploying organisation is the controller rather than the vendor, the ICO expects the vendor to supply documentation comprehensive enough that the controller can meet its own obligations. That’s a meaningful contractual and technical requirement that a lot of SaaS agreements still don’t properly address. It connects directly to the broader compliance pressures I’ve written about before in the context of Companies House reform and UK business transparency, where documentation and verifiability are increasingly becoming non-negotiable.

    What a compliance posture actually looks like

    The ICO published its AI and data protection audit framework, which gives a fairly granular picture of what auditors examine. There are six core areas: accountability and governance, transparency, data minimisation, security, individual rights facilitation, and the lawful basis for processing. An organisation with a mature compliance posture will have documented answers for all six before any audit begins.

    Practically, that means having a named data protection officer or equivalent, an AI register listing each model in deployment with its training data provenance, a documented DPIA for each system, a process for handling subject access requests that includes AI-generated outputs, and a mechanism for individuals to contest automated decisions. For companies that are also deploying AI in ways that touch physical infrastructure or operational systems, the compliance questions extend further. Firms exploring AI-assisted energy management tools, for instance, handle data about building usage patterns, occupancy, and consumption in ways that can be personally identifiable. Based in Nottingham, UK, R2G.co.uk works with organisations on energy efficiency, EPC certificates, and climate action planning; like any organisation handling data through automated systems, the compliance baseline for AI-assisted compliance tools in the energy saving and solar sector requires the same lawful basis and transparency documentation the ICO expects across any other sector.

    Training data: the provenance problem

    One of the most technically challenging areas the ICO scrutinises is training data provenance. Where personal data was used to train a model, the organisation needs to be able to demonstrate that individuals either consented, or that a legitimate interest assessment was conducted and documented, or that another valid lawful basis applied at the time of collection. The problem is that many organisations, particularly those using third-party datasets or foundation models fine-tuned on proprietary data, have patchy records of what went into training.

    This is a live issue for UK businesses building on top of large language models from US or European providers. Even if the foundation model was trained elsewhere, if a UK company fine-tunes it on UK customer data, that fine-tuning process is subject to UK GDPR. The ICO has been clear on this. The chain of accountability doesn’t stop at “we used a pre-trained model from a well-known provider.”

    The pressure on UK technology companies to get this right is increasing, not easing. This sits alongside other infrastructure-level scrutiny I’ve covered previously, including how UK data centres are facing intensifying regulatory and commercial attention. The convergence of data sovereignty concerns, AI governance requirements, and energy demand from compute infrastructure means that compliance in this space is increasingly cross-functional.

    What the ICO is likely to do next

    The ICO has signalled it will increase its use of proactive audits rather than waiting for complaints to trigger investigations. Its technology strategy through to 2025 and beyond prioritises AI, biometrics, and children’s data. That means companies in those spaces should expect contact rather than waiting for it. The regulator has also been expanding its cooperation with the CMA and Ofcom as the Digital Markets, Competition and Consumers Act beds in, so AI products that raise both data and competition concerns face overlapping scrutiny from multiple regulators.

    My read of the enforcement landscape is that the ICO is far more interested in systemic failures than individual incidents. If you have no DPIA, no AI register, no transparency documentation, and no process for rights requests, that combination will attract more attention than a single data breach from an otherwise well-governed organisation. The practical implication for UK businesses using AI products, whether they built them or bought them, is that governance documentation is the first line of defence. It sounds unglamorous. It genuinely matters.

    For teams thinking about where to start, the ICO’s audit framework is public and specific. Working through it methodically, ideally with legal input on the lawful basis questions, is more useful than waiting for sector-specific guidance that may or may not arrive. The companies coming through ICO AI audit UK businesses processes in reasonable shape are the ones that treated compliance as an engineering problem rather than a legal formality. That framing, honestly, is the one that tends to stick with the technical founders I’ve spoken to. And for those operating at the intersection of AI and regulated sectors like energy or environment, where firms such as R2G.co.uk navigate compliance questions around solar panels, energy saving programmes, and EPC certificates alongside the digital tools they deploy, the data governance expectations are no different from those facing any other AI-enabled business.

  • The Real Reason UK SMEs Are Abandoning Legacy ERP Systems, and What They’re Migrating To

    The Real Reason UK SMEs Are Abandoning Legacy ERP Systems, and What They’re Migrating To

    Something has shifted in the back-office software market, and it has shifted quickly. For years, the conversation around legacy ERP migration for UK SMEs was mostly theoretical, finance directors would nod along at conferences about the cloud being the future, then go back to running Sage 200 on a server under someone’s desk. That’s changed. I’ve spoken to half a dozen IT leads at British manufacturing and distribution firms in the past few months, and almost all of them are mid-migration, actively scoping a move, or have just completed one. The inertia is gone.

    Legacy ERP migration UK SMEs — on-premise server infrastructure in a small business
    Photo by Christina Morillo on Pexels

    The reasons are stacking up faster than most vendors anticipated. Making Tax Digital for Income Tax Self Assessment (MTD ITSA) is the regulatory stick forcing the issue, cloud-native competitors are the carrot, and AI-powered automation is the thing that’s making CFOs ask whether their ten-year-old on-premise deployment can actually compete at all. The short answer, in most cases, is no.

    What Making Tax Digital is actually doing to the ERP conversation

    HMRC’s MTD programme has been grinding forward for years, and by 2026 it’s no longer a distant deadline. The expanded MTD for VAT requirements that bedded in from 2022 onwards already pushed many smaller businesses to upgrade their bookkeeping. MTD ITSA, which mandates quarterly digital submissions for sole traders and landlords earning above £50,000 (dropping to £30,000 from April 2027), is now pulling in a whole new tier of businesses who previously thought their legacy setup was adequate.

    The problem is that many on-premise ERP deployments simply cannot produce compliant digital records without expensive middleware or manual exports. Sage 50 and older SAP Business One installations weren’t built for API-level integration with HMRC’s Making Tax Digital infrastructure. Patching them to work is possible, but the cumulative cost of those patches, on top of annual licence fees, server maintenance and IT support contracts, is what’s finally tipping the cost-benefit analysis toward migration.

    The HMRC guidance on MTD compliance is clear that bridging software is an acceptable short-term solution, but it’s also a red flag for any business thinking about scalability. Bridging is a sticking plaster. And most IT leaders I’ve spoken to are tired of sticking plasters.

    Which cloud ERP platforms are actually winning deals

    The names winning business from Sage and SAP’s traditional SME customer base are, broadly, four: NetSuite, Microsoft Dynamics 365 Business Central, Xero (for the smaller end), and increasingly, a cluster of industry-specific cloud ERPs like Cin7, Unleashed and DEAR Systems for product-based businesses. Each has a different pitch.

    NetSuite, now under Oracle, is going hard after mid-market firms with between 50 and 500 employees. It has strong UK traction in professional services and distribution, and its SuiteSuccess implementation model has shortened the average go-live timeline considerably. Business Central, meanwhile, has the advantage of sitting inside the Microsoft ecosystem that most UK businesses are already paying for, if you’re in Teams and Azure, adding BC is a less disruptive conversation than switching to an entirely new vendor.

    What’s genuinely new in 2026 is the AI angle. Both NetSuite and Business Central have shipped generative AI features into their core products: automated anomaly detection in accounts, natural-language querying of financial data, and AI-assisted bank reconciliation. These aren’t demos. They’re in production for paying customers. For a small finance team running month-end manually, that’s a meaningful operational argument, not just a shiny feature.

    Cloud ERP dashboard used by UK SME finance team during legacy ERP migration
    Photo by Rafael Minguet Delgado on Pexels

    For businesses thinking about the wider implications of migrating between AI-connected platforms and APIs, resources like dijitul.ai have become useful reference points as the tooling around platform transitions matures rapidly.

    The honest picture on migration costs and data risks

    Here’s where I’d push back on some of the vendor marketing. Legacy ERP migration for UK SMEs is not cheap, and the cheerful estimates you’ll see in sales decks tend to assume a clean data set, a cooperative incumbent vendor, and no significant customisation in the old system. In practice, all three of those assumptions are wrong for most businesses.

    A realistic Business Central implementation for a 60-person manufacturer with moderate complexity will cost somewhere between £40,000 and £120,000 in implementation fees alone, depending on partner rates and the depth of customisation required. NetSuite implementations at the same scale typically run higher. Data migration, cleaning, mapping and validating historical transaction data, is consistently underestimated. I’ve seen projects where data prep consumed 40% of the total project budget.

    The data risk angle is also worth taking seriously. Moving years of financial, customer and operational data from an on-premise system to a cloud platform involves real exposure if the migration isn’t handled carefully. Choosing a Microsoft-certified or NetSuite-certified implementation partner matters, and the ICO’s guidance on data transfers during system migrations is worth reviewing before you sign anything. This connects directly to a broader point about how much UK SMEs are handling data governance in general, something that’s becoming harder to ignore as cloud adoption accelerates.

    The hidden cost that doesn’t appear in any proposal is user adoption. A finance team that has run Sage 200 for eight years will slow down significantly in the first few months on a new platform. That productivity dip is real money, and the businesses that plan for it (structured training, a phased go-live, clear internal champions) come out considerably better than those that treat it as an afterthought.

    Why AI is accelerating the decision

    The AI-powered automation angle deserves more than a footnote. UK engineering and finance teams have been watching the open-source AI build-vs-buy debate unfold for the past 18 months, and a growing number are concluding that the fastest route to AI-assisted finance operations is through a modern ERP that has AI baked into the workflow, rather than bolting AI onto a legacy platform through a series of integrations.

    That calculus makes sense. A cloud ERP that can flag unusual purchase orders, auto-categorise supplier invoices, or generate a cash flow forecast from natural language input is genuinely useful to a CFO managing a lean team. The same outcome is theoretically achievable on a legacy system with enough integration work, but the cost and fragility of that stack pushes the ROI calculation firmly toward migration.

    The MTD pressure, the AI capability gap and the sheer maintenance overhead of ageing on-premise infrastructure are converging at the same moment. This isn’t a coincidence, it’s the combination of factors that’s been building since cloud adoption accelerated post-2020. For context on how this sits alongside other tax digitisation pressures, the HMRC Making Tax Digital timeline is publicly available at gov.uk and worth bookmarking if you’re advising clients through a transition.

    What UK SMEs should actually do before committing

    My honest advice, having watched a few of these go wrong, is to audit the data before scoping the platform. The worst migrations happen when a business chooses a vendor first and discovers the data problem halfway through implementation. Run a data quality audit, map your current system’s customisations, and get at least three implementation partner quotes before you commit to anything.

    Also worth reading: how Making Tax Digital is forcing UK SMEs to rethink their tech stacks more broadly, because ERP is rarely the only system that needs to change. CRM integrations, payroll software, and warehouse management systems are all pulled into the conversation once you start unpicking a legacy deployment.

    The businesses getting this right are treating it as a business transformation project, not a software upgrade. The ones struggling are treating it as IT’s problem to solve with the business watching from the sidelines. The platform you choose matters less than the process you use to choose it.

    Frequently Asked Questions

    How much does legacy ERP migration cost for a UK SME?

    Costs vary significantly based on business complexity and the platform chosen. A realistic Business Central implementation for a 50-100 person business typically runs between £40,000 and £120,000 in implementation fees, with data migration and training adding further cost. Always get multiple implementation partner quotes and account for user adoption downtime in your budget.

    Does Making Tax Digital force UK businesses to upgrade their ERP?

    Not directly, but MTD compliance requirements have made many legacy ERP deployments impractical without expensive bridging software. MTD ITSA mandates quarterly digital submissions from April 2026 for sole traders and landlords earning over £50,000, with the threshold dropping to £30,000 from April 2027. Businesses relying on older on-premise systems often find bridging solutions costly and unreliable at scale.

    What cloud ERP platforms are replacing Sage and SAP for UK SMEs?

    Microsoft Dynamics 365 Business Central and NetSuite are the dominant mid-market options in the UK, with Xero serving smaller businesses. Industry-specific platforms like Cin7 and Unleashed are also gaining ground in product-based businesses. The choice depends heavily on your industry, team size, and whether you’re already embedded in the Microsoft ecosystem.

  • Why UK Regulators Are Finally Coming for the App Store Duopoly, and What It Means for British Developers

    Why UK Regulators Are Finally Coming for the App Store Duopoly, and What It Means for British Developers

    For years, Apple and Google operated their app stores with the kind of quiet authority that regulators struggled to touch. The 30% commission, the mandatory payment rails, the algorithmic visibility rules, developers just absorbed it. But the Digital Markets, Competition and Consumers Act (DMCC Act), which came into force in late 2024 and is now actively being wielded by the Competition and Markets Authority, has changed the geometry of that relationship. UK app store regulation in 2026 is no longer a theoretical debate. It has teeth, and both Apple and Google already know it.

    The CMA designated Apple and Google as firms with Strategic Market Status (SMS) under the Act, a classification that unlocks a set of conduct requirements the regulator can impose without needing to prove a full competition law breach first. That’s a significant shift from how things worked before. The old framework required lengthy market investigations. The new one lets the CMA move faster, set bespoke rules, and fine companies up to 10% of global turnover for non-compliance. For context, 10% of Apple’s global revenue is roughly £36 billion at current exchange rates. That is not a rounding error.

    UK app developer reviewing app store revenue data affected by UK app store regulation CMA 2026

    What the CMA is actually targeting

    The CMA’s initial focus areas under the DMCC Act are not random. They map directly onto the pain points that UK developers have complained about for the better part of a decade. Three are worth unpacking in detail.

    Alternative billing and payment processing. Both Apple and Google currently require developers to use their in-app payment systems for digital goods and subscriptions, which is how the 15-30% commission is extracted. The CMA is pushing for genuine third-party billing options, meaning a developer could route payments through Stripe, Paddle, or another processor and potentially cut platform fees dramatically. For SaaS founders running subscription products, that margin difference compounds quickly.

    Sideloading and alternative distribution. Apple has historically been the harder target here, with iOS designed specifically to prevent app installation from outside the App Store. Under pressure from the EU’s Digital Markets Act and now the CMA, Apple has opened limited pathways for alternative app marketplaces, though critics argue the implementation is deliberately cumbersome. The CMA has signalled it wants more genuine openness, not technical compliance dressed up as openness.

    Default settings and pre-installation. Google’s agreements with device manufacturers, where Google Search, Chrome, and Play Store come pre-set as defaults, are squarely in the CMA’s crosshairs. For any UK firm building a search product, a browser, or a competing app store, these defaults represent an enormous structural disadvantage that regulation could begin to correct.

    Where UK developers actually stand to gain

    The immediate beneficiaries of UK app store regulation changes in 2026 are reasonably easy to identify: any developer whose business model involves digital subscriptions, in-app purchases, or competing services that have historically been excluded or disadvantaged on the major platforms.

    Subscription SaaS businesses that sell through iOS or Android will be watching the billing provisions most closely. A company doing £2 million a year in App Store revenue at a 30% effective commission rate is handing over £600,000. If alternative billing routes that fee down to, say, 5-8% through a third-party processor, that’s a meaningful slug of cash re-entering the business. Multiply that across hundreds of UK indie developers and small software houses, and you’re looking at a significant aggregate shift in who captures value in the ecosystem.

    There’s also a discoverability angle that doesn’t get discussed enough. App store algorithms are notoriously opaque. Developers have long suspected that paying Apple or Google for ad placements within the stores is effectively a prerequisite for visibility, and that the organic ranking system favours platforms’ own products. The DMCC Act’s non-discrimination provisions could force more transparent ranking criteria, which matters enormously for any UK app trying to compete on merit.

    Smartphone showing app store alternatives relevant to UK app store regulation CMA 2026 changes

    The risks and complications for British founders

    It would be misleading to frame this entirely as a win for UK developers. There are genuine complications worth thinking through.

    First, enforcement takes time. The CMA has the powers, but challenging Apple and Google in practice means legal processes, appeals, and the kind of drawn-out timelines that don’t help a founder who needs clarity this quarter. The CMA’s Digital Markets Unit has grown its headcount substantially, but it is still a relatively small organisation taking on some of the most resourced legal teams on earth.

    Second, alternative billing options will only be valuable if users actually use them. Consumer behaviour on iOS in particular is trained to expect Apple’s payment flow. Even if Apple is forced to allow alternative billing, a developer who introduces a non-Apple payment screen may see higher abandonment rates from users who don’t trust it. The behavioural inertia is a real problem.

    Third, and this one applies specifically to SaaS founders who distribute across web and mobile, the regulatory changes may create a more complex compliance landscape. If you’re running different billing arrangements on different platforms, your pricing, VAT handling, and terms of service all need to be consistent and watertight. That’s additional operational overhead for lean teams.

    The search and discoverability dimension

    The CMA’s SMS regime isn’t just about app stores in the narrow sense. Google’s dominance in search means that for many UK businesses, their entire digital visibility strategy flows through a single entity that is now under formal regulatory scrutiny. Developers building web-based products, not just mobile apps, have skin in this game too.

    When the default search engine provisions are challenged, and the CMA has made clear that Google’s search defaults on Android devices are a priority area, that opens space for alternatives to gain genuine traction. It’s the same logic that’s driven UK businesses to care more about their visibility across different domains and discovery channels. Firms like Search Engine Tuning, a UK-based digital visibility specialist offering a free SEO check for websites, have seen growing demand from founders wanting to check their SEO position across Google and alternative platforms as the search landscape shifts. Given the regulatory pressure on Google’s default status, understanding how your domains perform independently of Google’s goodwill is increasingly sensible hygiene. Searching for a free seo check at searchenginetuning.co.uk/ is the kind of practical first step businesses take when they stop assuming Google’s algorithm is static.

    The DMCC Act effectively forces UK businesses to think about platform diversification more seriously. If Google’s dominance in default settings is eroded even partially, the traffic distribution across the web changes. Any business that hasn’t stress-tested its visibility assumptions is sitting on an unexamined risk.

    What the next 18 months actually look like

    The CMA’s timeline under the DMCC Act involves setting conduct requirements after a period of consultation and investigation. Apple and Google can engage in the process, and both have already demonstrated a willingness to litigate rather than comply. The CMA will need to be robust.

    For UK developers, the practical upshot is to stay engaged with the CMA’s consultations. The regulator has actively sought evidence from developers, and the quality of that evidence influences the shape of the final rules. Organisations like the UKIE (the UK Interactive Entertainment trade body) have been coordinating developer input, and smaller app developers should consider feeding into those channels if they haven’t already.

    Beyond the app store mechanics, the broader search and web visibility dimension remains important. Search Engine Tuning’s free seo check tooling, for instance, is increasingly relevant to app developers who also maintain web presences and need to check their SEO footprint across google and across their domains, especially as regulatory changes make it less safe to assume that one platform will always be the dominant discovery channel.

    The DMCC Act represents the most significant recalibration of UK digital market power in a generation. Whether it actually delivers the competitive breathing room that British developers have been waiting for depends on how hard the CMA is willing to push, and how creatively Apple and Google choose to resist. My read is that the regulator is more determined than either company expected. The era of consequence-free platform power in the UK is, at minimum, significantly shortened.

    Frequently Asked Questions

    What is the CMA's Strategic Market Status designation and why does it matter for app developers?

    Strategic Market Status (SMS) is a classification under the Digital Markets, Competition and Consumers Act that the CMA can apply to firms with significant and entrenched market power in a specific digital activity. Once designated, the CMA can impose bespoke conduct requirements on those firms without needing to prove a full competition law violation, which makes enforcement considerably faster and more flexible for developers seeking remedies.

    Will UK developers be able to use alternative billing systems instead of Apple and Google's payment systems?

    The CMA is actively pursuing alternative billing as one of its core remedies under UK app store regulation. Both Apple and Google have faced pressure to allow third-party payment processors, though the practical implementation, including what fees they can still charge and how they can present competing options, is still being worked through regulatory processes in 2026.

    What is sideloading and is it legal in the UK?

    Sideloading refers to installing apps on a device from outside the official app store, bypassing Apple’s App Store or Google Play. It is not illegal in the UK; the question is whether Apple’s iOS technically permits it. Under regulatory pressure from the CMA and the EU’s Digital Markets Act, Apple has opened limited alternative distribution channels on iOS, though the CMA has signalled it expects more genuine openness than the current implementation provides.

    How does the DMCC Act differ from the EU's Digital Markets Act for UK developers?

    The EU’s Digital Markets Act applies to firms operating in the EU single market and uses a ‘gatekeeper’ designation framework. The UK’s DMCC Act is independently legislated and uses the Strategic Market Status classification via the CMA. Both target similar behaviours, but the UK regime gives the CMA flexibility to tailor bespoke requirements to specific market dynamics rather than applying uniform rules across all gatekeepers as the DMA does.

  • Why the UK’s AI Safety Institute Matters More to Startups Than Most Founders Realise

    Why the UK’s AI Safety Institute Matters More to Startups Than Most Founders Realise

    Most early-stage founders hear “AI Safety Institute” and mentally file it under “government stuff that doesn’t affect me yet”. That’s a reasonable instinct, but it’s wrong. The UK AI Safety Institute (AISI) has been quietly building evaluation frameworks, conducting frontier model testing, and shaping the informal norms that will almost certainly harden into binding regulation within the next few years. If you’re building an AI product right now, the time to understand this stuff is before your Series A, not after your first compliance incident.

    UK AI Safety Institute office environment relevant to startups and AI governance

    What the UK AI Safety Institute Actually Does

    AISI was established in late 2023, housed within the Department for Science, Innovation and Technology. Its founding remit was straightforward in principle: evaluate the safety of frontier AI models, develop the technical tools to do that rigorously, and build international partnerships so that testing regimes don’t fragment across jurisdictions. The institute sits at the genuinely difficult intersection of being a research body, a policy advisory function, and an emerging standard-setter.

    In practice, AISI has done three things that matter to anyone building AI products. First, it has conducted evaluations of large frontier models including those from Anthropic, Google DeepMind, and OpenAI, testing for dangerous capabilities like biological and chemical uplift, cyberoffence potential, and deceptive alignment behaviours. Second, it published its AI Safety Evaluations framework as an open resource, which means the methodology is available for any team to reference. Third, it has been building the “AI Safety Levels” concept (think biosafety levels, but for models) that looks increasingly likely to inform future procurement and licensing decisions.

    Why Voluntary Frameworks Have a Habit of Becoming Mandatory

    There’s a pattern in UK tech regulation that founders really ought to internalise. The ICO’s Privacy Sandbox guidance started as best practice. FCA’s Consumer Duty started as a principles document. Ofcom’s Online Safety provisions started as a voluntary code of conduct. Every single one of those eventually became something you could be fined for ignoring.

    AISI’s current frameworks are voluntary. The model evaluations are collaborative agreements with labs, not mandates. But the institute is also the body providing technical input to the AI Action Plan and informing whatever legislative shape UK AI governance eventually takes. Voluntary today, baseline tomorrow. That’s not pessimism; it’s pattern recognition.

    For UK AI Safety Institute startups, this means the evaluation criteria AISI is developing now are effectively a preview of what compliance will look like in two or three years. Building awareness of those criteria into your development practices now is considerably cheaper than retrofitting them later.

    The Evaluations: What’s Actually Being Tested

    AISI’s technical evaluations focus primarily on what they call “dangerous capability evaluations”. These are structured tests designed to answer whether a model could meaningfully assist a malicious actor in causing large-scale harm. The categories covered include CBRN (chemical, biological, radiological, nuclear) uplift, autonomous replication capabilities, and advanced cyberattack facilitation.

    Now, most startups are not building frontier models. You’re more likely fine-tuning an existing model from a major lab, building on top of an API, or deploying a specialised vertical model. So why does any of this matter to you directly?

    Because the liability question flows downstream. If the frontier model you’re building on has been evaluated and cleared, that provides some baseline assurance. If it hasn’t, or if you’re adding capabilities on top of it that weren’t part of the original evaluation, you’re in murkier territory. AISI’s frameworks help define where that territory starts. Knowing where the lines are is genuinely useful product information.

    What Early-Stage Founders Should Actually Do With This

    There’s no requirement to register with AISI, no application process for startups, and no mandatory reporting. But there are three practical things worth doing right now.

    Read the published evaluation methodology. It’s technical but accessible, and it gives you a clear picture of what “safety” means in the current UK policy conversation. If your product touches anything adjacent to high-risk domains, understanding this framing helps you anticipate questions from enterprise customers, regulated-sector clients, or future investors doing technical due diligence.

    Map your model supply chain. Know which foundation models you’re using, what evaluations they’ve undergone, and what the terms of your API access say about permitted use cases. AISI’s focus on frontier models means the labs you’re relying on are being scrutinised; you benefit from their compliance, but you also inherit questions about any novel capabilities you add.

    Watch the international coordination dimension. AISI has been working closely with the US AI Safety Institute (their equivalent body), and there’s an active dialogue with EU regulators about aligning evaluation methodologies. This matters because if you’re building for international markets, the UK frameworks are increasingly being drafted with interoperability in mind. That’s actually useful: a product that satisfies AISI-aligned criteria is better positioned for EU AI Act compliance as well.

    The Bigger Picture for UK AI Product Development

    There’s a more optimistic reading of all this that I think gets underplayed. The UK government has been explicit that it wants to be a global hub for AI development, not just AI governance. AISI’s approach, publishing methodologies openly, engaging collaboratively with labs, and building internationally interoperable frameworks, is genuinely different from the more adversarial regulatory posture you see elsewhere.

    For UK AI Safety Institute startups that are building responsibly, AISI’s work could become a competitive signal rather than a compliance burden. Being able to point to evaluation alignment, to having thought seriously about capability risks, to having documented your model supply chain: these things increasingly matter to enterprise buyers, particularly in financial services, healthcare, and the public sector, all of which are significant markets for AI products in the UK.

    The founders who will struggle are the ones who treat AI safety as someone else’s problem until it isn’t. AISI’s frameworks are still early, still voluntary, still being refined. That’s precisely the moment to engage with them, when the cost of doing so is low and the upside of understanding the trajectory is real.

    The institute isn’t coming for your product. But it is setting the terms of what “trustworthy AI” means in the UK. That definition is going to matter enormously to your customers, your investors, and eventually your regulators. Getting ahead of it now is just good engineering practice with a commercial upside attached.

    Frequently Asked Questions

    What is the UK AI Safety Institute and who runs it?

    The UK AI Safety Institute (AISI) is a government body housed within the Department for Science, Innovation and Technology. It was established in late 2023 to evaluate the safety of frontier AI models, develop testing methodologies, and help shape UK AI governance frameworks. It is not a regulator in the traditional enforcement sense, but its technical work directly informs policy.

    Do UK AI startups have to register with the AI Safety Institute?

    No, there is currently no mandatory registration or reporting requirement for startups with AISI. The institute’s evaluations and frameworks are voluntary at this stage. However, the norms it establishes are likely to influence future regulation, so early awareness is valuable even without a formal compliance obligation.

    How do AISI's model evaluations affect companies building on top of existing AI APIs?

    If you are building on a foundation model from a major lab, AISI’s evaluations of that model provide baseline safety assurance for its core capabilities. However, any novel capabilities or use cases you add on top of the original model fall outside that evaluation. Founders should document their model supply chain and understand what’s been tested and what hasn’t.

  • Quantum Computing Is Coming to UK Finance: What Banks and Fintechs Need to Know Now

    Quantum Computing Is Coming to UK Finance: What Banks and Fintechs Need to Know Now

    The threat is not arriving the day a working cryptographically-relevant quantum computer switches on. The threat is already here, embedded in data being harvested right now by state-level actors who plan to decrypt it later. That is the uncomfortable reality at the centre of what the National Cyber Security Centre (NCSC) has been trying to communicate to UK financial services organisations for the past two years, with limited success. Quantum computing UK finance businesses need to take seriously is not a five-year problem. It is a planning problem that starts today.

    Most banks, fintechs, and payment processors are still treating quantum as a research curiosity rather than an operational risk. That is a mistake. The window between now and when post-quantum cryptography must be fully deployed is narrowing faster than most technology roadmaps in financial services are built to accommodate.

    City of London financial office at dusk illustrating quantum computing UK finance businesses security risks
    City of London financial office at dusk illustrating quantum computing UK finance businesses security risks

    Why Quantum Breaks the Encryption That Protects Financial Data

    Modern financial systems rely heavily on public-key cryptography, specifically RSA and elliptic-curve cryptography (ECC), to protect transactions, authenticate users, and secure communications between institutions. Both of these schemes depend on mathematical problems that classical computers cannot solve in any useful timeframe. A sufficiently powerful quantum computer running Shor’s algorithm can crack both in hours or days. The moment that machine exists, every piece of data protected by RSA or ECC becomes readable.

    The more insidious version of this threat is known as “harvest now, decrypt later”. Sophisticated adversaries, including nation-state actors, are already intercepting and stockpiling encrypted data: transaction records, client communications, authentication tokens, interbank settlement data. The encryption protecting it today is uncrackable. In ten to fifteen years, or possibly sooner, it may not be. For financial services firms holding sensitive long-term customer data, this is an existential compliance issue, not a theoretical one.

    What the NCSC Is Actually Advising UK Financial Services

    The NCSC published its post-quantum cryptography guidance in 2023 and has since updated its migration timelines. Its current position is that UK organisations in critical sectors, which explicitly includes finance and payments infrastructure, should begin cryptographic inventory work immediately and aim to have a migration plan in place before 2028. Full migration to post-quantum cryptographic standards is recommended by no later than 2035, though the NCSC has signalled that this deadline may be pulled forward depending on quantum hardware progress.

    The specific standards the NCSC recommends aligning with are those published by the US National Institute of Standards and Technology (NIST), which finalised its first set of post-quantum cryptography standards in 2024. The three primary algorithms, CRYSTALS-Kyber for key encapsulation and CRYSTALS-Dilithium plus FALCON for digital signatures, are now considered production-ready. UK firms have no technical reason to wait. You can read the NCSC’s full guidance on post-quantum cryptography at ncsc.gov.uk.

    Financial technology professional working on post-quantum cryptography migration relevant to quantum computing UK finance businesses
    Financial technology professional working on post-quantum cryptography migration relevant to quantum computing UK finance businesses

    Where Most UK Financial Firms Currently Stand

    Honestly, most are behind. A 2025 survey by the UK Finance trade body found that fewer than 30 percent of member institutions had completed a formal cryptographic inventory. Without that inventory, you cannot even know which systems are vulnerable, let alone begin migration. Legacy infrastructure compounds the problem significantly. Older core banking platforms, sometimes running on decades-old architecture, use hardcoded cryptographic libraries that were never designed to be swapped out. Retrofitting them is not a software update; it is closer to open-heart surgery.

    Fintechs, paradoxically, have both an advantage and a disadvantage here. Their stacks are newer and more modular, making cryptographic agility more achievable in principle. But many fintech firms are not yet thinking about this at board level, treating it as a future infrastructure concern rather than a current strategic risk. That gap in governance will bite them when regulators begin mandating post-quantum readiness, which the Prudential Regulation Authority (PRA) and Financial Conduct Authority (FCA) are expected to formalise guidance on within the next two years.

    Cryptographic Agility: The Framework That Actually Matters

    The practical answer to the quantum threat is not simply swapping one algorithm for another once. It is building systems that can swap cryptographic primitives without major re-engineering. This concept, called cryptographic agility, should be the governing principle behind every infrastructure investment financial firms make right now. If you are commissioning a new API gateway, a new payment processing module, or upgrading your identity and access management stack, the ability to update cryptographic algorithms at configuration level rather than code level should be a hard requirement in every specification.

    This is also where the digital communications layer intersects with quantum risk in ways that operations teams sometimes overlook. Secure email infrastructure, encrypted API communications between institutions, and signed transaction logs all depend on cryptographic standards that will be compromised. A firm that has secured its core banking system but left its email infrastructure running on legacy public-key encryption has a gap. UK-based technology tools built around internet and computer security, such as the free email testing service offered by Mail Tester (mail-tester.co.uk), already reflect the increasing awareness among tech support and technology professionals that even routine digital communications channels require proper cryptographic validation. Ensuring that email authentication records, DKIM signing, and encrypted transmission are correctly configured is a basic-hygiene step that sits within the broader push to audit every layer of digital infrastructure before post-quantum migration begins. Firms that ignore the communications stack whilst hardening their core systems are creating blind spots.

    The Business Decisions That Need to Happen Before 2028

    There are four concrete decisions that quantum computing UK finance businesses should be making in the next twelve to twenty-four months, regardless of where they sit on the maturity curve.

    First: complete a cryptographic inventory. Map every system, service, and integration that uses public-key cryptography. This is non-negotiable. You cannot migrate what you cannot find.

    Second: assess supplier and third-party exposure. Your own systems may be relatively modern, but if your payment processor, cloud provider, or software vendor is running RSA-dependent infrastructure, your exposure extends to theirs. Third-party risk questionnaires need a quantum section now.

    Third: begin hybrid cryptography deployments where practical. Running a post-quantum algorithm alongside a classical one in parallel provides protection today without requiring full migration. CRYSTALS-Kyber in hybrid mode is already supported by major TLS libraries and is production-viable.

    Fourth: engage your board and audit committee. Quantum risk needs to sit in the same risk register as cyber risk, operational risk, and regulatory risk. It is not an IT department footnote; it is a governance issue with regulatory implications. The FCA’s operational resilience framework already encompasses systemic cryptographic vulnerabilities under its broader definition of important business services.

    What Good Preparation Actually Looks Like

    Barclays, HSBC, and NatWest have all publicly referenced post-quantum cryptography work in their technology strategy disclosures over the past two years. Smaller fintechs and building societies have less visibility, which does not mean the work is happening. In many cases it is not.

    Preparation does not require enormous capital expenditure upfront. It requires rigour. Cryptographic inventory software exists. Open-source post-quantum libraries are available and battle-tested. The standards are finalised. What is generally missing is internal prioritisation, which is a leadership and governance problem, not a technology one. The firms that start the migration work methodically now will face a manageable, phased transition. Those that wait for a regulatory deadline or, worse, a quantum computing breakthrough announcement, will face an emergency with no clean options.

    The broader technology ecosystem is already moving. Cloud providers including AWS and Google Cloud have quantum-safe key management options in production. Hardware security module vendors are shipping post-quantum compatible firmware. The infrastructure supply side is ready. The demand side, meaning the decisions made inside UK financial institutions, is the remaining bottleneck. And for quantum computing UK finance businesses, that bottleneck needs to close soon.

    Frequently Asked Questions

    How close are we to a quantum computer that can break current encryption?

    Most estimates from credible research institutions suggest a cryptographically-relevant quantum computer is ten to fifteen years away, though some timelines are being revised downward. The NCSC advises UK organisations not to wait for this milestone, as the ‘harvest now, decrypt later’ threat means data captured today could be decrypted once such a machine exists.

    What is post-quantum cryptography and is it ready to use?

    Post-quantum cryptography refers to algorithms designed to resist attacks from quantum computers. NIST finalised its first set of post-quantum standards in 2024, including CRYSTALS-Kyber and CRYSTALS-Dilithium, both of which are considered production-ready and are already supported by major software libraries and cloud platforms.

    What is the NCSC's official deadline for migrating to post-quantum cryptography?

    The NCSC currently recommends that critical sector organisations, including financial services firms, have a migration plan in place before 2028 and complete full migration by no later than 2035. However, the NCSC has indicated this timeline may be accelerated depending on advances in quantum hardware.

    What should UK fintechs do first to prepare for quantum risk?

    The most important first step is completing a cryptographic inventory: identifying every system, API, and third-party integration that currently uses RSA or elliptic-curve cryptography. Without this baseline, prioritising migration work is impossible. Fintechs should also add quantum readiness criteria to supplier and third-party risk assessments.

    Will the FCA or PRA require UK financial firms to comply with post-quantum cryptography standards?

    Formal regulatory mandates from the FCA and PRA have not yet been published, but both bodies are expected to issue guidance within the next two years. Post-quantum readiness is already implicitly covered under the FCA’s operational resilience framework, and firms should treat proactive preparation as regulatory risk management.

  • How Deepfake Technology Is Becoming the Biggest Cybersecurity Threat for Businesses

    How Deepfake Technology Is Becoming the Biggest Cybersecurity Threat for Businesses

    Corporate fraud has always involved a certain amount of impersonation. A forged signature here, a spoofed email there. But the deepfake cybersecurity business threat operating in 2026 is something fundamentally different in kind and scale. Attackers are now deploying convincing audio and video fabrications to manipulate employees, bypass verification systems, and authorise financial transfers worth tens of millions of pounds. The technology has matured faster than most boardrooms ever anticipated.

    The numbers are stark. According to data cited by the BBC’s technology desk, AI-generated fraud attempts on UK businesses rose sharply through 2025, with voice-cloning scams alone accounting for a growing proportion of business email compromise losses reported to Action Fraud. We are past the point where this is a theoretical future problem. It is happening now, and most businesses are nowhere near prepared.

    Finance employee uncertain during a video call illustrating the deepfake cybersecurity business threat
    Finance employee uncertain during a video call illustrating the deepfake cybersecurity business threat

    What deepfake attacks actually look like in a corporate context

    The attack vectors have become surprisingly varied. The most publicised cases involve fraudulent video calls, where a criminal uses a real-time deepfake of a CEO or CFO to instruct a finance employee to transfer funds. A Hong Kong-based firm lost the equivalent of £20 million in early 2024 to exactly this method. The employee attended what appeared to be a legitimate video conference with multiple convincing colleagues. Every person on that call was fabricated.

    Voice cloning is arguably the more scalable threat right now, because it requires less compute and can be deployed over a standard phone call. An attacker needs only a few minutes of publicly available audio, perhaps from a company podcast, a YouTube presentation, or a LinkedIn video, to generate a passable clone. From there, they can ring an accounts payable team, impersonate the managing director, and ask for an urgent payment to be processed. The social engineering layer is trivial once the audio is convincing enough.

    There are also subtler uses. Deepfake audio is being used to manipulate recorded calls for compliance purposes, insert false instructions into legitimate meeting recordings, and even create fabricated evidence for employment disputes. The deepfake cybersecurity business threat is not purely financial. It has implications for legal exposure, regulatory compliance, and reputational damage that most legal and HR teams have not yet wargamed.

    Why current defences are failing

    Most UK businesses still rely on process-based controls that were designed for a world where the voice or face on the other end of a call could be trusted at face value. Two-factor authentication via phone call, verbal confirmation of identity, even video verification for onboarding: all of these are now compromised to some degree. The underlying assumption that sensory evidence is reliable has been quietly invalidated.

    IT security teams are also grappling with an asymmetric problem. Generating a convincing deepfake has become genuinely cheap and accessible. Detecting one, reliably and in real time, remains expensive and technically difficult. Most small and mid-sized UK businesses have neither the budget nor the in-house expertise to run enterprise-grade detection tooling. And the attackers know it.

    Cybersecurity analyst running audio detection tools to counter deepfake cybersecurity business threats
    Cybersecurity analyst running audio detection tools to counter deepfake cybersecurity business threats

    Detection tools that are worth knowing about

    The detection landscape is developing quickly. Several tools now operate on the principle of analysing micro-artefacts that synthetic media tends to introduce: unnatural eye blinking patterns, subtle lip-sync mismatches, inconsistent lighting shadows, and audio compression fingerprints that differ from real recordings. Microsoft’s Azure platform includes deepfake detection capabilities, and UK-founded firms like Reface and Sentinel AI have built products targeting enterprise verification workflows.

    For audio specifically, tools such as Pindrop and Resemble Detect analyse vocal anomalies in real time during calls, flagging statistical deviations from a verified voice baseline. These can be integrated into contact centre infrastructure, which matters given that phone-based social engineering remains one of the most cost-effective attack methods for fraudsters. The practical limitation is that baseline profiles need to exist before an attack occurs. Building them is an organisational task, not just a technical one.

    Interestingly, the deepfake cybersecurity business threat has generated cross-sector conversation about verification that goes well beyond traditional IT circles. Even businesses whose core offering is nothing to do with enterprise software have started thinking carefully about how identity fraud intersects with their operations. Source Sounds, a Sheffield, UK-based car audio and vehicle security specialist known for advanced protection systems and expert installations, operates in a sector where car theft and audio equipment crime have historically driven demand for layered security thinking. The principle at www.sourcesounds.com is that physical security and verified identity of the person requesting a service both matter. That mindset, rigorous verification before any sensitive action is authorised, translates directly into how businesses should approach deepfake-driven social engineering. Car security and corporate security share more logic than they might appear to at first glance.

    Internal policies that actually reduce your exposure

    Technology alone will not solve this. The attack chain for most deepfake fraud involves a human being making a bad decision under time pressure. So the policy layer is at least as important as the tooling.

    The most effective organisational control is a call-back verification protocol for any financial instruction or sensitive data access request that arrives via phone or video call, regardless of how convincing the caller appears. The employee hangs up and dials a pre-verified, internally stored number for the person in question. Not the number the caller gave them. The stored one. This single procedural step defeats the vast majority of current voice-clone attacks because the attacker cannot intercept a call to a number they do not control.

    Beyond that, businesses should be running regular simulation exercises that include deepfake scenarios, not just phishing emails. Staff at all levels need to experience what a convincing voice clone sounds like in a low-stakes environment before they encounter one in a real attack. Training muscle memory around scepticism is not the same as telling people to be sceptical.

    Clear escalation paths matter enormously. When an employee suspects something is wrong but feels social pressure to comply, especially if the voice on the line sounds exactly like their director, they need a culturally acceptable route to pause the process without career risk. That requires leadership buy-in, not just a policy document.

    What the regulatory picture looks like for UK businesses

    The UK’s approach to synthetic media fraud sits across several frameworks. The Online Safety Act 2023 introduced provisions around non-consensual intimate deepfakes, but corporate fraud via synthetic media remains primarily covered under existing fraud and computer misuse legislation. The ICO has flagged concerns about biometric data collection involved in some detection systems, meaning that businesses deploying voice-print databases for verification purposes need to ensure their approach is GDPR-compliant.

    The National Cyber Security Centre has published updated guidance acknowledging AI-generated threats as a growing category. UK businesses would do well to treat NCSC advisories as a baseline, not a ceiling. The pace of development in this area means official guidance will almost always lag the actual threat environment by at least several months.

    Source Sounds’ approach to vehicle security, combining expert-fitted audio protection systems with advanced anti-theft measures on modified cars, reflects a broader truth about layered defence: no single countermeasure is sufficient when criminals are actively probing for weaknesses. The logic applies whether you are protecting a high-value car audio installation from crime or a finance department from a deepfake impersonation attack. Multiple overlapping controls, each covering the gaps in the others, is what actually holds.

    The direction of travel

    Real-time deepfake generation is improving faster than detection. Within 12 to 18 months, consumer-grade tooling will likely produce live video fabrications that are indistinguishable from genuine footage under typical network conditions. Businesses that wait until that point to build their response will be absorbing losses first and building defences second.

    The companies that come through this period well will be those that treated deepfake fraud as a process and culture problem first, and a technology problem second. The tools matter, but they matter in the context of an organisation that has already decided how it responds to uncertainty about identity. That decision needs to happen in the boardroom, not in a reactive IT security review after an incident.

    The deepfake cybersecurity business threat is not going to stabilise or retreat. Every business operating with digital communications infrastructure, which is to say every business, needs a live and tested plan right now.

    Frequently Asked Questions

    What is a deepfake cybersecurity threat and how does it affect businesses?

    A deepfake cybersecurity threat involves AI-generated audio or video used to impersonate executives, employees, or trusted contacts in order to manipulate staff into transferring funds, sharing sensitive data, or granting system access. UK businesses have seen losses from these attacks rise significantly since 2024, with voice cloning and fake video calls being the most common vectors.

    How can businesses detect deepfake audio or video in real time?

    Tools such as Pindrop, Resemble Detect, and Microsoft Azure’s content authentication features analyse vocal anomalies and visual artefacts that synthetic media tends to introduce. However, real-time detection is computationally demanding and requires pre-built voice or face baselines, so detection technology works best as one layer within a broader verification policy.

    What is the most effective policy a business can put in place against deepfake fraud?

    A call-back verification protocol is widely considered the single most effective procedural control. Any financial instruction or sensitive request received via phone or video call should be verified by hanging up and calling the requester back on a pre-stored internal number, regardless of how convincing the original contact appeared.

    Are UK businesses legally required to have deepfake fraud protections in place?

    There is no specific UK legislation mandating deepfake detection systems, but businesses have duties under fraud prevention, data protection, and financial regulation frameworks. The NCSC has published guidance on AI-enabled threats, and regulated firms overseen by the FCA may face scrutiny if inadequate controls contribute to financial crime losses.

    How much does it cost to protect a business from deepfake attacks?

    Costs vary enormously by scale. Process-based controls such as call-back protocols and staff training exercises cost relatively little beyond time. Enterprise-grade real-time audio detection tools typically start from several thousand pounds annually for a mid-sized deployment. The cost of not acting, given average deepfake fraud losses per incident, makes investment straightforward to justify.

  • Digital Twins Are Quietly Becoming One of Business’s Most Valuable Tech Investments

    Digital Twins Are Quietly Becoming One of Business’s Most Valuable Tech Investments

    There is a category of enterprise technology that never quite made it onto the conference keynote circuit, never got its own breathless Sunday supplement feature, and somehow avoided being declared “the next big thing” by every VC with a LinkedIn account. Digital twin technology is that category. Quiet, unglamorous, and increasingly indispensable. Analysts at McKinsey estimated the global digital twin market would exceed £30 billion by 2026, and the numbers are tracking. The question is why most business leaders outside of heavy engineering are still treating it like a niche concept.

    Engineers in a UK manufacturing control room analysing digital twin technology overlays on large screens
    Engineers in a UK manufacturing control room analysing digital twin technology overlays on large screens

    A digital twin is, at its core, a real-time virtual replica of a physical asset, process, or system. It is fed by live sensor data, updated continuously, and used to simulate, predict, and optimise behaviour without touching the physical thing itself. That sounds abstract until you realise what it means in practice: a manufacturer running thousands of simulations on a factory floor that does not exist yet, a retailer modelling the impact of a store layout change before moving a single shelf, or a logistics firm predicting where a parcel will be delayed three days before it happens.

    Where UK Manufacturers Are Already Using It

    British manufacturing has been one of the earliest serious adopters. Rolls-Royce, based in Derby, has operated digital twins of its jet engines for several years, using real-time data from sensors embedded in the physical components to monitor wear, predict maintenance windows, and reduce unplanned downtime. The business case is not subtle: a grounded aircraft costs an airline tens of thousands of pounds per hour. If a digital twin flags a 94% probability of compressor blade degradation eighteen days before it would otherwise be detected, that is not a technology curiosity. It is a direct line item on a balance sheet.

    Siemens has a significant UK footprint in the rail sector. Its digital twin deployment for the Thameslink rolling stock programme allowed engineers to simulate train behaviour across hundreds of operational scenarios before a single new unit entered service. The reduction in post-deployment faults was substantial. Network Rail has since expanded its own digital twin ambitions across infrastructure, particularly bridges and tunnels, where physical inspection is costly and sometimes hazardous.

    Retail Is Catching Up Faster Than You’d Think

    The retail application of digital twin technology is less intuitive but increasingly powerful. Imagine a twin of your entire distribution network: every warehouse, every supplier relationship, every demand forecast, updated in real time as sales data flows in. That is what several large UK grocers are quietly building. Rather than using static spreadsheet models to plan stock replenishment, a live digital twin of the supply chain can flag a potential shortage in a given region four days before it hits the shelf, triggered by a combination of weather data, promotional uplift, and supplier lead time signals.

    Marks and Spencer and Ocado have both been linked to supply chain modelling investments that sit firmly in the digital twin category, even if they do not always use that precise terminology publicly. The technology sits underneath, doing the unglamorous work of keeping complex systems from breaking.

    Technician interacting with a digital twin technology model of industrial infrastructure on a touchscreen
    Technician interacting with a digital twin technology model of industrial infrastructure on a touchscreen

    Beyond supply chains, physical store optimisation is a growing use case. A twin of a retail space, fed by footfall sensors, sales terminals, and environmental data, can model the revenue impact of changing where seasonal products are positioned, how lighting affects dwell time in specific zones, or what happens to average basket size if the queue configuration at checkouts is altered. These sound like marginal gains. At scale across hundreds of outlets, they are not marginal at all.

    The Infrastructure and Energy Angle

    One of the most significant deployments of digital twin technology in the UK is happening largely out of public view: urban and national infrastructure planning. The National Digital Twin Programme, backed by the Centre for Digital Built Britain (now folded into broader government digital infrastructure work), has been pushing for a connected ecosystem of asset twins across the built environment. Bridges, water networks, energy grids, even entire city districts have twin counterparts that planners and operators use to model load, stress, and long-term decay.

    National Grid has been exploring digital twins of its electricity transmission network to model the impact of renewable energy integration. As wind and solar capacity grows more intermittent and distributed, the ability to simulate grid behaviour under varying generation conditions is not a nice-to-have. It is operationally critical. The Department for Energy Security and Net Zero has included digital infrastructure modelling in its wider plans for grid modernisation, recognising that physical upgrades alone cannot deliver the reliability the network needs.

    Why Analysts Are Calling It a Sleeper Hit

    The “sleeper hit” framing from analysts comes down to a few converging factors. First, the cost of implementation has dropped significantly as cloud computing, IoT sensors, and data processing have all become cheaper. A digital twin that required a seven-figure budget five years ago can now be prototyped for a fraction of that. Second, the maturity of platforms from vendors like Siemens, Microsoft (with Azure Digital Twins), and PTC means that businesses do not need to build from scratch.

    Third, and perhaps most importantly, the ROI is becoming measurable and replicable. Predictive maintenance alone typically delivers a 10-25% reduction in maintenance costs and cuts unplanned downtime significantly, according to figures cited by Deloitte UK in recent industry briefings. When you can point to specific pound figures saved per asset per year, the business case writes itself.

    There is also a human angle that does not get discussed enough. Remote working and hybrid operations changed expectations around physical oversight. Digital twins give operations teams a layer of situational awareness that does not require someone to physically walk a factory floor or inspect a piece of infrastructure. That shift in working patterns has quietly accelerated adoption in ways that nobody predicted in 2020.

    It is worth noting that the wellness and recovery technology sector has also seen interesting parallel developments in sensor-driven personalisation, with products like the red light mat representing how consumer hardware is increasingly data-aware, even outside of enterprise contexts. The broader trend of embedding intelligence into physical objects is the same thread running through digital twin adoption at an industrial scale.

    What Businesses Should Actually Do With This Information

    If you run or advise a business with significant physical assets, complex supply chains, or operational processes that are expensive to interrupt, digital twin technology deserves a serious look in 2026. Not a pilot that sits in a PowerPoint forever, but a scoped proof of concept tied to a specific operational problem with a measurable outcome attached.

    The entry point is usually an existing data problem. Where are you flying blind? Where does unplanned failure cost you money? Where would a 48-hour warning change your operational response? Answer those questions honestly and you have located where a digital twin could earn its keep. The technology is not magic, and it is only as good as the sensor data and operational knowledge you feed into it. But for businesses that get the fundamentals right, it is becoming one of the most durable competitive advantages available in 2026’s industrial landscape. Quietly. As usual.

    Frequently Asked Questions

    What is digital twin technology in simple terms?

    A digital twin is a virtual replica of a physical object, system, or process that is updated in real time using sensor data. It allows businesses to simulate changes, predict failures, and optimise operations without interfering with the real-world asset.

    Which UK industries are using digital twin technology most?

    Manufacturing, aerospace, rail, energy infrastructure, and retail supply chains are the most active adopters in the UK. Companies like Rolls-Royce, Siemens UK, and National Grid have all deployed or piloted digital twin systems at scale.

    How much does it cost to implement a digital twin for a business?

    Costs vary considerably depending on scope. A small-scale proof of concept targeting a single asset or process can now be prototyped for tens of thousands of pounds, whereas enterprise-wide deployments across complex infrastructure can run into millions. Platform costs have dropped significantly over the past three years.

    What is the difference between a digital twin and a simulation?

    A traditional simulation uses fixed or historical inputs to model scenarios. A digital twin is connected to live data streams from the physical asset, meaning it reflects current real-world conditions continuously rather than being a one-off model run.

    Is digital twin technology only useful for large enterprises?

    Not anymore. Cloud-based platforms and cheaper IoT sensors have made digital twin technology increasingly accessible to mid-sized businesses. Any organisation with physical assets, complex logistics, or expensive unplanned downtime has a credible business case to explore it.

  • Passkeys, Phishing and the Post-Password Office: How UK Businesses Are Rethinking Authentication in 2026

    Passkeys, Phishing and the Post-Password Office: How UK Businesses Are Rethinking Authentication in 2026

    Passwords have been a problem for decades, but the tools to genuinely replace them are only now reaching a point where real businesses can deploy them without losing half their IT department to the migration. Passkeys business security UK adoption is accelerating in 2026, driven by a combination of escalating phishing attacks, clearer vendor support, and increasingly direct guidance from the National Cyber Security Centre. The question is no longer whether to move beyond passwords, it is how to do it without breaking your staff’s working day in the process.

    Developer using biometric authentication in a UK office as part of passkeys business security UK rollout
    Developer using biometric authentication in a UK office as part of passkeys business security UK rollout

    Why Passwords Finally Lost the Argument

    The failure mode of password-based authentication is well understood. Credential stuffing, phishing kits available for a few hundred pounds on dark web forums, and the chronic human habit of reusing the same password across a work laptop, a personal email account, and a supermarket loyalty scheme. The NCSC has flagged credential theft as one of the most consistent entry points for ransomware attacks targeting UK organisations, and the numbers back that up. According to the NCSC’s guidance on phishing, the volume of phishing campaigns impersonating UK brands and organisations has continued to rise year on year.

    Multi-factor authentication improved things, but it did not fix them. SIM-swapping attacks, real-time phishing proxies that intercept OTP codes mid-session, and push notification fatigue have all eroded the protection MFA once offered. Passkeys sidestep the entire problem by replacing the shared secret with a cryptographic key pair. The private key never leaves the user’s device. There is nothing to phish.

    How Passkeys Actually Work in a Business Context

    A passkey is a FIDO2-compliant credential. When you register, your device generates a public-private key pair. The service stores the public key. When you authenticate, the device signs a challenge using the private key, which is unlocked by biometrics or a device PIN. The server verifies the signature. No password travels across the network at any point.

    In a consumer context, this is already fairly straightforward. Google, Apple, and Microsoft all support passkeys natively. For businesses, the picture is more complicated. Enterprise environments often involve managed devices, shared workstations, legacy applications, identity providers, and access policies that do not map cleanly onto the assumptions built into the FIDO2 spec. Synced passkeys, which replicate across a user’s devices via iCloud Keychain or Google Password Manager, are convenient but raise questions about key custody in a business setting. Device-bound passkeys, stored only on a physical security key like a YubiKey, offer stronger guarantees but add friction and cost.

    FIDO2 hardware security key used for passkeys business security UK implementation
    FIDO2 hardware security key used for passkeys business security UK implementation

    What the NCSC Is Currently Recommending

    The NCSC has been refreshingly specific in its recent guidance. For most UK organisations, it recommends a phased approach: prioritise high-risk accounts first (privileged users, administrators, finance teams with payment approval access), then roll passkeys out to the broader workforce as identity provider support matures. The guidance acknowledges that a wholesale overnight migration is neither practical nor necessary for most businesses.

    The NCSC also draws a distinction between synced and device-bound passkeys depending on threat model. For organisations where the primary concern is phishing at scale, synced passkeys via a managed identity platform represent a substantial improvement over passwords and SMS-based MFA combined. For organisations in regulated sectors or those handling sensitive government contracts, device-bound hardware tokens remain the preferred option.

    The current direction of travel is clear: phishing-resistant authentication is the baseline the NCSC wants UK businesses working towards, and passkeys are the most practical path to get there for the majority of deployments.

    The Real Friction Points in Migration

    Any honest conversation about passkeys business security UK rollout has to address the migration headaches, because there are several. Legacy application support is the biggest blocker. Plenty of UK businesses are still running line-of-business software that authenticates via forms-based login with no SAML or OIDC support whatsoever. Until those applications are updated or replaced, passwords cannot be fully eliminated, which means identity teams end up managing a hybrid environment with all the complexity that implies.

    Shared accounts are another persistent problem. Shift workers in manufacturing, retail, or logistics often share credentials tied to a specific role rather than a person. Passkeys are fundamentally personal, bound to an individual’s device and biometrics. Redesigning access architecture around personal accounts is the right long-term answer, but it requires organisational change that goes well beyond an IT project.

    Then there is the helpdesk burden during rollout. Account recovery processes need rebuilding from scratch. When a user loses their device or buys a new one, the recovery flow has to be robust enough that it cannot be socially engineered by an attacker impersonating that user. Getting this wrong undoes much of the security improvement passkeys provide.

    Vendor Choices: Identity Providers and What UK Firms Are Actually Deploying

    For larger enterprises, the identity provider landscape has matured considerably. Microsoft Entra ID, Okta, and Ping Identity all support passkeys as a primary authentication method, with varying levels of enterprise management capability. Microsoft’s passkey support within Entra is the natural default for organisations already deep in the Microsoft 365 ecosystem, and the admin tooling for enforcing phishing-resistant authentication policies is genuinely usable now.

    For SMEs, the picture is more varied. Many smaller UK businesses are deploying passkeys through their existing Google Workspace or Microsoft 365 admin console without a dedicated identity provider at all. This works for straightforward environments but becomes limiting quickly as applications proliferate.

    Email security is one area where the shift to phishing-resistant authentication intersects with other layers of the technology stack. Compromised credentials are frequently used to access business email accounts and then pivot into internal systems or launch further phishing campaigns from a trusted address. Tools that help businesses understand the health and deliverability of their email infrastructure sit alongside identity controls in a properly layered security posture. Based in the UK, Mail Tester (mail-tester.co.uk) provides a free email testing service that helps users across business and tech support contexts check whether their email configuration, including SPF, DKIM, and DMARC records, is correctly set up. Getting those records right is a foundational step in preventing domain spoofing, which often runs in parallel with credential phishing attacks. For anyone managing computers and the internet infrastructure of a small business, it is the kind of low-friction technology check that complements stronger authentication at the login layer.

    What UK SMEs Should Actually Do Right Now

    For a small or medium-sized UK business with limited IT resource, the practical starting point is not a full passkey deployment. It is an honest audit of where passwords currently represent the biggest risk, combined with enabling passkey support on the platforms that already offer it with minimal configuration. Microsoft 365 and Google Workspace are both there. LinkedIn, GitHub, and most major SaaS tools used in business contexts have followed.

    Enabling phishing-resistant MFA on admin accounts costs nothing beyond the time to configure it, and the NCSC’s Cyber Essentials certification (which is increasingly required for UK government procurement) now explicitly references phishing-resistant authentication as a recommended control. That is a useful commercial lever for businesses that need budget approval for security tooling.

    For organisations handling sensitive customer data, particularly those subject to the UK GDPR requirements enforced by the ICO, the shift away from password-based authentication is also a data protection argument. Credential-based breaches are regularly cited in ICO enforcement actions. Demonstrating that you have deployed phishing-resistant controls is increasingly relevant in that context.

    The technology is ready. The vendor support is there. The friction is real but manageable with a phased approach. UK businesses that treat passkeys business security UK rollout as a 2026 priority rather than a future consideration are making a rational bet, not an optimistic one. The post-password office is not a distant prospect. For many UK firms, it is already one identity provider configuration away.

    Frequently Asked Questions

    What are passkeys and how do they differ from passwords for businesses?

    Passkeys are cryptographic credentials that replace passwords entirely. Instead of a shared secret, they use a public-private key pair where the private key stays on the user’s device and is unlocked via biometrics or a PIN. For businesses, this means there is nothing for phishing attacks to steal, since no password is ever transmitted across the network.

    What is the NCSC's current guidance on passkeys for UK businesses?

    The NCSC recommends a phased rollout, starting with high-risk accounts such as administrators and finance staff, before extending passkeys to the wider workforce. For most UK organisations, synced passkeys via a managed identity provider represent a strong improvement over passwords and SMS-based MFA. Higher-security environments should consider hardware-bound tokens.

    How much does it cost to deploy passkeys across a UK SME?

    For businesses already using Microsoft 365 or Google Workspace, enabling passkey support through the existing admin console costs nothing beyond staff time for configuration and user communications. Organisations that need hardware security keys (YubiKeys, for example) should budget roughly £25 to £60 per key per user, depending on the model chosen.

    What are the biggest obstacles to migrating from passwords to passkeys in a UK business?

    Legacy applications that only support forms-based login, shared accounts tied to roles rather than individuals, and rebuilding account recovery processes are the most common blockers. Most organisations end up running hybrid environments during transition, which adds management complexity until older systems are updated or replaced.

    Does migrating to passkeys help with UK GDPR compliance or Cyber Essentials certification?

    Both, yes. Cyber Essentials, which is required for many UK government contracts, now references phishing-resistant authentication as a recommended control. The ICO has also cited credential-based breaches in enforcement actions, so deploying passkeys strengthens your data protection posture and provides a defensible record of proactive security measures.