Category: The Futures Bright

  • The Compliance-by-Design Playbook: How UK Fintechs Are Building Regulation Into Their Architecture From Day One

    The Compliance-by-Design Playbook: How UK Fintechs Are Building Regulation Into Their Architecture From Day One

    There’s a phrase I’ve been hearing a lot in engineering conversations lately: “compliance by design”. It sounds like the kind of thing a consultant puts on a slide deck to justify their day rate. In practice, though, compliance by design in UK fintech is reshaping how teams hire, which tools they buy, and what actually makes it onto the product roadmap. The firms getting this right aren’t bolting legal requirements onto a finished product. They’re threading them through the architecture from the first pull request.

    This isn’t just neat engineering philosophy. The FCA’s Consumer Duty, which came into full force in July 2023, combined with tightening Anti-Money Laundering obligations and the ever-present requirements of UK data protection law, has created a regulatory environment where post-hoc compliance is genuinely too expensive to sustain. I’ve spoken to engineers and product leads at several UK fintechs over the past few months, and the picture that emerges is consistent: the compliance team is no longer the department that shows up six weeks before launch to say no. They’re in the sprint.
    Software engineer reviewing compliance by design UK fintech architecture on dual monitors
    Photo by Daniil Komov on Pexels

    What Consumer Duty is actually demanding from engineering teams

    The FCA’s Consumer Duty is framed in outcome-based language, which sounds flexible until you realise that the FCA expects firms to evidence those outcomes. That evidencing requirement is the technical challenge. A fintech offering a credit product, for instance, must demonstrate that customers are genuinely understanding the product features, not just clicking through a disclosure screen. That distinction forces engineering decisions: you need instrumentation, you need journey analytics, you need a data model that can reconstruct a customer’s decision-making path on request.

    One product lead I spoke to at a mid-sized London-based lending platform described rebuilding their onboarding flow entirely around this requirement. “We had to ask ourselves: if the FCA walked in tomorrow and asked us to prove that a customer in financial difficulty understood the total cost of borrowing before they accepted, could we show that? The answer was no. So we rebuilt the logging architecture before we touched the UI.” That sequencing, infrastructure before interface, is the engineering expression of compliance by design.

    AML obligations are changing how data is modelled at schema level

    Anti-Money Laundering requirements have always demanded transaction monitoring, but the sophistication of what regulators now expect has shifted the problem from a rules engine bolted on top of a database to something that has to be designed into the data model from the start. UK fintechs operating under FCA-supervised AML frameworks need to maintain audit trails, flag unusual patterns in near-real time, and produce Suspicious Activity Reports that are coherent and complete. If your transaction data is spread across five microservices with inconsistent identifiers, you cannot do that reliably.

    The practical consequence is that AML compliance is now a forcing function for better data architecture. Firms that have invested in event-sourced systems and centralised entity resolution are finding that regulatory demands and engineering quality are pulling in the same direction. Those that haven’t are finding that every new compliance requirement creates disproportionate engineering debt. I’d argue this is one of the more underappreciated dynamics in the UK fintech space right now: regulation is quietly selecting for firms with mature engineering cultures.

    How this is changing hiring decisions

    The hiring implications are significant. UK fintech engineering teams are increasingly looking for what some are calling “compliance-aware” engineers: people who understand why a data retention policy affects how you design a deletion cascade, or why an audit log needs to be immutable rather than just append-only. This is distinct from hiring compliance officers into engineering teams, though some firms are doing that too. It’s more about raising the baseline expectation of what a senior backend engineer or data engineer should understand.

    This connects to the broader shift UK tech firms are navigating around hybrid skill sets and salary benchmarking. A fintech that needs an engineer who can design a schema that satisfies both a product requirement and a Subject Access Request workflow is fishing in a smaller talent pool than one looking for a standard backend hire. Some firms are compensating by pairing engineers with in-house legal or compliance specialists in dedicated squads, running what amounts to a regulatory interpretation layer directly inside the engineering organisation.

    Recruitment agencies I’ve spoken to note that fintech-specific compliance knowledge is now appearing in job specifications where previously it would have been absent. One specialist recruiter described it as “the GDPR moment all over again”, referring to the wave of data protection awareness that reshaped hiring briefly in 2018 and 2019, except this time it’s sticking because the FCA is actively supervising outcomes rather than just issuing guidance.

    Data protection requirements and the product roadmap

    UK data protection law, administered by the ICO, adds another layer. Subject Access Requests, data minimisation obligations, and the right to erasure all have to work in a financial services context where you also have a legal obligation to retain certain records for five or six years. Reconciling these requirements isn’t a legal problem; it’s an engineering problem. The solution tends to involve separating personal data from transactional records at the architectural level, using pseudonymisation or reference identifiers that can be severed without corrupting the audit trail.

    This kind of architectural decision has direct product roadmap consequences. Features that require enriching customer profiles with third-party data, for instance, now carry a compliance cost that product teams have to price in. I’ve seen fintech product roadmaps where compliance review of a proposed feature sits at the same priority level as engineering scoping. That’s a cultural shift as much as a technical one, and it doesn’t happen without deliberate organisational design.

    It’s worth noting that the ICO’s increasing focus on AI-driven products adds a further dimension. Firms using machine learning in credit decisions or fraud detection need to be able to explain those decisions in terms a customer can understand, which constrains model choice and demands additional logging infrastructure. The ICO’s AI audit programme is already asking firms to demonstrate exactly this kind of explainability, and the fintechs that have built compliance by design into their ML pipelines are finding those conversations considerably less stressful than those who haven’t.

    Tooling choices that reflect the shift

    On the tooling side, the compliance-by-design approach is driving adoption of specific categories of infrastructure. Immutable audit logging platforms, workflow automation tools that enforce four-eyes approval for sensitive operations, and data lineage tooling that maps where personal data lives across a system are all seeing increased uptake among UK fintechs. Some teams are building bespoke compliance dashboards that surface real-time metrics the FCA might ask about: complaint rates segmented by product feature, vulnerability flags by customer cohort, that sort of thing.

    There’s also a knock-on effect on the choice between build and buy. A fintech that has embedded compliance deeply into its architecture often finds that off-the-shelf SaaS components need significant adaptation to fit, because those products weren’t designed with UK regulatory specifics in mind. That’s a real tension, and it’s one of the reasons some UK fintechs have started reconsidering their infrastructure choices from first principles rather than assembling a stack of third-party products and hoping the compliance gaps can be papered over later.

    The firms that treat Consumer Duty, AML and data protection as engineering constraints from the start, rather than legal checklists to be satisfied at the end, are building faster in the medium term because they’re not constantly refactoring to accommodate the next regulatory update. That’s the real return on compliance by design in UK fintech: not just staying on the right side of the FCA, but building a codebase that doesn’t fall over every time the rulebook changes.
  • How the Online Safety Act Is Quietly Reshaping Product Decisions at UK Tech Startups

    How the Online Safety Act Is Quietly Reshaping Product Decisions at UK Tech Startups

    There is a version of this story where the Online Safety Act is a big-company problem. Where it is Ofcom versus Meta, a regulatory spat fought out by teams of lawyers billing four-figure day rates. That version is wrong. I have spoken to founders running community platforms with fewer than 50,000 monthly active users who are already rewriting roadmaps because of it. The Online Safety Act UK startups need to understand is not a future compliance checkbox. It is a live product constraint, and it is biting now.

    Startup founder reviewing product decisions affected by the Online Safety Act UK startups framework
    Photo by Walls.io on Pexels

    What Ofcom is actually doing in 2026

    Ofcom published its illegal harms duties guidance earlier this year, and the phasing is tighter than many founders realise. The first wave covers illegal content: child sexual abuse material, terrorism, fraud-enabling content. The second wave extends into systemic protections for children. The third covers transparency reporting for larger services. But the category thresholds that determine which duties apply are not purely about size. They factor in risk profile. A marketplace for second-hand goods that allows direct messaging between strangers could be categorised differently from a read-only publication with ten times the traffic.

    That risk-profile framing is the bit product teams are wrestling with. A UK-built community forum, a local buy-and-sell app, a creator platform for niche hobbyists: all of them sit in a grey zone where the letter of the Act might not obviously apply but the spirit, and Ofcom’s likely interpretation, very much does.

    The three product decisions that come up most often

    Moderation tooling

    Pre-Act, a lot of small UK platforms ran on reactive moderation: users flag, humans review, content comes down. That model does not satisfy the Act’s requirement to have systems that identify illegal content proactively. You need tooling that scans at upload or post time, not just when someone complains. For a bootstrapped startup, that is a real infrastructure cost. The honest answer for most founders I have talked to is that they are integrating third-party moderation APIs, Microsoft Azure Content Moderator and similar services, rather than building in-house. Which is pragmatic, but it does introduce a dependency and a data-sharing question that needs its own privacy assessment.

    User verification

    Age assurance is the area generating the most heated product debates. If your platform is likely to be accessed by under-18s and hosts content that could harm them, you need age assurance that is more than a tick-box. Ofcom has been deliberately non-prescriptive about method, which sounds flexible until you realise it means your team has to make and document a defensible choice. Mobile network operator age checks, credit reference lookups, document verification: each carries user friction, drop-off risk and cost. I would argue the startups getting this right are the ones treating age assurance as a UX problem first, not a compliance checkbox, because the solutions that minimise friction tend to be the ones that actually work at scale.

    There is a separate issue for marketplace products. Verifying that sellers are who they say they are is partly an Online Safety Act question and partly a fraud question. Services like 0lly track how fraudulent seller accounts operate on UK platforms, which gives a useful lens on why verification gaps are not just a regulatory risk but a trust and safety one that bleeds into your product reputation.

    Feature design and defaults

    The Act has a strong preference for safe defaults: settings that protect users unless they actively choose otherwise. For community and social products, this affects things like direct messaging between strangers, public profile discoverability and content recommendation algorithms. A UK startup building a local events app told me they had removed the ability for non-connected users to message each other entirely, replacing it with a host-mediated contact system. It was a significant product change. They made it before they hit any regulatory threshold because their legal counsel advised the risk of not doing it outweighed the feature value.

    Content moderation tooling interface relevant to Online Safety Act UK startups compliance
    Photo by cottonbro studio on Pexels

    The compliance infrastructure problem for small teams

    Here is what the guidance documents do not say clearly enough: the Act requires documentation. A risk assessment. A record of the steps you have taken. Ofcom cannot audit every small platform simultaneously, but when something goes wrong on your platform, you will need to demonstrate you had a system in place. For a four-person product team, that is not a trivial ask on top of shipping features.

    The UK’s tech startup ecosystem has seen a wave of compliance tooling built specifically around this gap. Companies like Crisp (the content moderation API) and Veriff (identity verification) have onboarding flows now explicitly pitched at Online Safety Act compliance for sub-scale platforms. The market has moved faster than most founders expected.

    There is a useful parallel with what happened to UK tech firms when GDPR came in. The immediate reaction was panic, followed by a lot of box-ticking, followed by a smaller group of companies realising that genuine privacy-by-design was a product differentiator. I think the same cycle happens here. The platforms that treat safety infrastructure as a feature rather than a tax will attract users and investors who care about it, and right now that cohort is growing. For founders navigating ICO compliance alongside AI feature development, layering Online Safety Act obligations on top feels brutal. But the tooling overlap is real.

    What investors are starting to ask

    I have seen term sheets from UK VCs in the past six months that include specific due diligence questions about Online Safety Act readiness. Not for Series B companies. For pre-seed and seed rounds on community and marketplace products. The question is usually framed around regulatory risk: “What is your exposure if Ofcom issues an enforcement notice and requires significant platform changes?” It is the same logic that drives questions about data residency and GDPR documentation. Investors have learnt, the hard way, that regulatory technical debt is real debt.

    For founders preparing financial models for investor conversations, building a moderation and compliance cost line into your operating expenditure is not optional anymore. If your pitch deck has no mention of trust and safety infrastructure, expect the question in the room.

    The tension with growth metrics

    Here is the uncomfortable part. A lot of the product changes the Online Safety Act requires will hurt short-term growth metrics. Friction in the sign-up flow reduces conversion. Removing public direct messaging reduces engagement. Proactive content moderation generates false positives that frustrate users and generate support tickets. None of this is fatal, but all of it requires a product team willing to trade a short-term metric hit for a longer-term structural sound platform.

    The startups I have seen handle this best are the ones that reframe the constraint early. Age assurance becomes “trust signals that make adult users feel safer sharing”. Moderation tooling becomes “the infrastructure that lets us grow into regulated verticals like education or healthcare”. Safe defaults become “the design system that prevents the kind of incident that kills a community platform overnight”. It is not spin. It is genuine product thinking applied to a compliance requirement.

    Practical steps for founders right now

    If you are building a UK platform with any user-generated content or user-to-user communication, the minimum viable compliance posture looks something like this: complete a service risk assessment using Ofcom’s published framework, document it, and revisit it quarterly. Choose a moderation API and integrate it before you hit the thresholds that make it legally required, so you have operational data on how it performs. Make a documented decision on age assurance and record the reasoning. Review your default settings against the “safety by design” principle and log the rationale for each choice you keep.

    None of this is as complicated as it sounds. The no-code tooling that UK councils have adopted for internal compliance workflows is increasingly available to small product teams too. Airtable bases tracking moderation incidents, Notion wikis documenting design decisions, Zapier automations pulling flagged content into a review queue: these are not enterprise solutions but they work for a team of five managing a platform of 20,000 users.

    The Online Safety Act is not going away, and Ofcom has made it clear enforcement will scale as platforms scale. The founders who treat that as a product problem to solve now will be in a materially better position than those who wait until the compliance notice arrives.

    Frequently Asked Questions

    Does the Online Safety Act apply to small UK startups and not just big platforms?

    Yes. The Act applies to any service with user-generated content or user-to-user communication that is accessible in the UK, regardless of company size. Ofcom’s duties are risk-based, so a small platform with high-risk features can face significant obligations even with a modest user base.

    What does Ofcom require for age assurance under the Online Safety Act?

    Ofcom has not mandated a single method, but platforms likely accessed by under-18s must use age assurance that is technically robust, rather than a simple self-declaration tick box. Accepted approaches include mobile network operator checks, credit reference lookups, and document verification. Platforms must document their choice and the reasoning behind it.

    How much does Online Safety Act compliance cost a startup?

    Costs vary significantly by platform type and feature set. Third-party moderation APIs typically run from a few hundred pounds a month for low-volume platforms to several thousand for high-volume ones. Identity verification APIs from providers like Veriff or Yoti charge per verification, often in the range of £0.50 to £2 per check. The documentation and risk assessment work is largely an internal time cost.

    What happens if a UK startup ignores the Online Safety Act?

    Ofcom can issue enforcement notices requiring specific changes, impose fines of up to £18 million or 10% of global annual revenue (whichever is higher), and in serious cases seek court orders to block services. Senior managers can also face personal liability for certain failures involving child safety provisions.

    How is the Online Safety Act different from GDPR for UK product teams?

    GDPR is primarily about how you collect, store and process personal data. The Online Safety Act is about the harm potential of your platform’s features and content. The two frameworks overlap in areas like user identity and data processing for moderation, so compliance work on one often informs the other, but they have distinct risk assessments, documentation requirements and regulators.

  • Why the UK’s Semiconductor Strategy Is More Relevant to Software Founders Than They Realise

    Most software founders I speak to have a version of the same reaction when you mention the UK semiconductor strategy: a polite nod, followed by a rapid mental retreat to something that feels more immediately relevant, like pricing models or burn rate. Semiconductors are a hardware problem, right? Someone else’s problem. The chips arrive, the cloud runs, the code ships.

    That framing is going to cost people money. The UK’s National Semiconductor Strategy, published in 2023 and still actively shaping industrial policy in 2026, has direct implications for AI inference costs, hardware procurement timelines, and the supply chain risks sitting quietly underneath every British tech business that touches compute. Founders who treat it as background noise are missing something practical.

    What the strategy actually says, stripped of the policy language

    The headline number is £1 billion committed over a decade to strengthen the UK’s position in semiconductor design, research, and supply chain resilience. That sounds significant. In global context it is, frankly, modest. The US CHIPS Act committed roughly $52 billion. The EU Chips Act targets €43 billion. The UK is not trying to out-manufacture Taiwan or South Korea. The strategy is explicit about this: Britain’s comparative advantage is in chip design and intellectual property, not fabrication at scale.

    What that means in practice is that UK government money is flowing towards university research, compound semiconductor development (particularly in Wales, at Cardiff University’s Institute for Compound Semiconductors), and design ecosystem support. It is not building a fleet of fabs that will produce the GPUs your inference workloads run on. Those will still come predominantly from TSMC in Taiwan and Samsung in South Korea, assembled into finished boards by Nvidia, AMD, or their upstream partners, and then rented to you via AWS, Google Cloud, or Azure data centres, many of which are already among the most contested real estate in Britain.

    Why inference costs are a semiconductor problem in disguise

    Here is the bit that catches people off guard. When you run an LLM inference call, or a vision model, or any serious AI workload, the cost you pay to a cloud provider reflects, amongst other things, the global supply and demand picture for the chips powering those servers. GPU allocation has been constrained for two years. The wait time for reserved H100 capacity on major cloud platforms stretched to months in 2024. That has eased somewhat, but the structural dependency on a geographically concentrated supply chain has not.

    UK tech startups building AI-native products are directly exposed to this. I’ve seen founding teams price their AI features based on inference costs at signing, only to find those costs shift materially within two quarters because chip supply tightened again or a new model generation changed the hardware economics entirely. This is not purely a cloud pricing story. It is a semiconductor supply story, and the UK’s ability to influence it is limited precisely because our strategy is focused upstream, on design IP, not downstream on fabrication capacity.

    The supply chain resilience question for British businesses

    There is a more immediate concern sitting behind the strategic one. UK businesses that buy physical hardware, whether server boards for on-premises inference, edge compute devices, or industrial embedded systems, sit near the end of a very long supply chain that runs through East Asia. The disruptions of 2020 to 2022 are supposedly resolved, but the concentration risk is structurally unchanged.

    For most pure software businesses this is theoretical. For anyone building hardware-adjacent products, running their own inference infrastructure, or operating in sectors like manufacturing, defence, or telecoms, it is operational risk that belongs in a proper risk register. The UK strategy does address this through its Supply Chain Audit Programme and through engagement with the new Semiconductor Advisory Panel, but these are coordination mechanisms, not solutions to physical geography.

    There is an indirect benefit worth flagging. The UK’s focus on compound semiconductors, particularly gallium nitride and silicon carbide, matters for power electronics and radio frequency applications. If your product sits in the telecoms, energy, or IoT space, British research in these materials is closer to your world than you might think. The UK’s gigabit broadband rollout depends on exactly this class of semiconductor for base station power amplifiers. That is a concrete domestic market signal.

    What this means for hardware availability and procurement

    The practical procurement picture for UK tech businesses in 2026 looks like this. GPU compute via cloud remains the path of least resistance for most startups, but pricing volatility is real and worth modelling explicitly. Reserved capacity contracts are worth the overhead if your inference volumes are predictable. Spot instances remain a gamble on the wrong side of a supply crunch.

    For companies considering on-premises inference, whether for data sovereignty reasons, latency, or pure economics at scale, hardware lead times for Nvidia and AMD server products remain longer than the official line suggests. UK distributors I’ve spoken to informally put realistic delivery windows at 12 to 20 weeks for enterprise GPU configurations, depending on the quarter. That matters for product roadmap planning in a way that deserves honest budget conversations, not just a line in a Gantt chart. The kind of financial modelling discipline that UK founders are increasingly applying to investor readiness should extend to hardware procurement timelines too.

    The talent and IP angle founders keep missing

    The part of the UK semiconductor strategy that has the clearest near-term upside for software founders is the design and IP ecosystem. Britain has genuine world-class chip design capability, centred on Arm’s architecture (still headquartered in Cambridge), and a cluster of fabless design companies that are producing interesting work in specialist processors, edge inference chips, and neuromorphic architectures.

    This matters because the next generation of inference hardware may not look like a datacentre GPU. Companies like Graphcore (Bristol) and Groq’s UK-connected research threads represent a design tradition that could produce inference silicon better suited to specific workloads. Founders building for the long term, particularly in edge AI or embedded applications, should be watching this ecosystem closely. The UK strategy’s investment in research talent also connects to the broader talent dynamics reshaping UK tech hiring, as chip design roles command premiums that are pulling engineering graduates in directions that affect the whole pipeline.

    My take on what founders should actually do

    The UK semiconductor strategy is not a document worth reading cover to cover unless policy analysis is genuinely your thing. But the conditions it reflects and partly shapes are worth understanding at a practical level. Run a proper sensitivity analysis on your inference costs under a supply constraint scenario. If you are buying physical hardware, build procurement lead times into your planning that reflect reality rather than optimism. Track what is happening with UK-originated chip design companies, because the inference hardware landscape in three to five years could look meaningfully different from today’s GPU monoculture.

    The UK is not going to manufacture its way to semiconductor independence. But it might design its way into a position where British-originated IP powers the next wave of efficient inference chips. For software founders, that is worth at least one line in your technology radar.

  • The Real Reason UK SMEs Are Abandoning Legacy ERP Systems, and What They’re Migrating To

    The Real Reason UK SMEs Are Abandoning Legacy ERP Systems, and What They’re Migrating To

    Something has shifted in the back-office software market, and it has shifted quickly. For years, the conversation around legacy ERP migration for UK SMEs was mostly theoretical, finance directors would nod along at conferences about the cloud being the future, then go back to running Sage 200 on a server under someone’s desk. That’s changed. I’ve spoken to half a dozen IT leads at British manufacturing and distribution firms in the past few months, and almost all of them are mid-migration, actively scoping a move, or have just completed one. The inertia is gone.

    Legacy ERP migration UK SMEs — on-premise server infrastructure in a small business
    Photo by Christina Morillo on Pexels

    The reasons are stacking up faster than most vendors anticipated. Making Tax Digital for Income Tax Self Assessment (MTD ITSA) is the regulatory stick forcing the issue, cloud-native competitors are the carrot, and AI-powered automation is the thing that’s making CFOs ask whether their ten-year-old on-premise deployment can actually compete at all. The short answer, in most cases, is no.

    What Making Tax Digital is actually doing to the ERP conversation

    HMRC’s MTD programme has been grinding forward for years, and by 2026 it’s no longer a distant deadline. The expanded MTD for VAT requirements that bedded in from 2022 onwards already pushed many smaller businesses to upgrade their bookkeeping. MTD ITSA, which mandates quarterly digital submissions for sole traders and landlords earning above £50,000 (dropping to £30,000 from April 2027), is now pulling in a whole new tier of businesses who previously thought their legacy setup was adequate.

    The problem is that many on-premise ERP deployments simply cannot produce compliant digital records without expensive middleware or manual exports. Sage 50 and older SAP Business One installations weren’t built for API-level integration with HMRC’s Making Tax Digital infrastructure. Patching them to work is possible, but the cumulative cost of those patches, on top of annual licence fees, server maintenance and IT support contracts, is what’s finally tipping the cost-benefit analysis toward migration.

    The HMRC guidance on MTD compliance is clear that bridging software is an acceptable short-term solution, but it’s also a red flag for any business thinking about scalability. Bridging is a sticking plaster. And most IT leaders I’ve spoken to are tired of sticking plasters.

    Which cloud ERP platforms are actually winning deals

    The names winning business from Sage and SAP’s traditional SME customer base are, broadly, four: NetSuite, Microsoft Dynamics 365 Business Central, Xero (for the smaller end), and increasingly, a cluster of industry-specific cloud ERPs like Cin7, Unleashed and DEAR Systems for product-based businesses. Each has a different pitch.

    NetSuite, now under Oracle, is going hard after mid-market firms with between 50 and 500 employees. It has strong UK traction in professional services and distribution, and its SuiteSuccess implementation model has shortened the average go-live timeline considerably. Business Central, meanwhile, has the advantage of sitting inside the Microsoft ecosystem that most UK businesses are already paying for, if you’re in Teams and Azure, adding BC is a less disruptive conversation than switching to an entirely new vendor.

    What’s genuinely new in 2026 is the AI angle. Both NetSuite and Business Central have shipped generative AI features into their core products: automated anomaly detection in accounts, natural-language querying of financial data, and AI-assisted bank reconciliation. These aren’t demos. They’re in production for paying customers. For a small finance team running month-end manually, that’s a meaningful operational argument, not just a shiny feature.

    Cloud ERP dashboard used by UK SME finance team during legacy ERP migration
    Photo by Rafael Minguet Delgado on Pexels

    For businesses thinking about the wider implications of migrating between AI-connected platforms and APIs, resources like dijitul.ai have become useful reference points as the tooling around platform transitions matures rapidly.

    The honest picture on migration costs and data risks

    Here’s where I’d push back on some of the vendor marketing. Legacy ERP migration for UK SMEs is not cheap, and the cheerful estimates you’ll see in sales decks tend to assume a clean data set, a cooperative incumbent vendor, and no significant customisation in the old system. In practice, all three of those assumptions are wrong for most businesses.

    A realistic Business Central implementation for a 60-person manufacturer with moderate complexity will cost somewhere between £40,000 and £120,000 in implementation fees alone, depending on partner rates and the depth of customisation required. NetSuite implementations at the same scale typically run higher. Data migration, cleaning, mapping and validating historical transaction data, is consistently underestimated. I’ve seen projects where data prep consumed 40% of the total project budget.

    The data risk angle is also worth taking seriously. Moving years of financial, customer and operational data from an on-premise system to a cloud platform involves real exposure if the migration isn’t handled carefully. Choosing a Microsoft-certified or NetSuite-certified implementation partner matters, and the ICO’s guidance on data transfers during system migrations is worth reviewing before you sign anything. This connects directly to a broader point about how much UK SMEs are handling data governance in general, something that’s becoming harder to ignore as cloud adoption accelerates.

    The hidden cost that doesn’t appear in any proposal is user adoption. A finance team that has run Sage 200 for eight years will slow down significantly in the first few months on a new platform. That productivity dip is real money, and the businesses that plan for it (structured training, a phased go-live, clear internal champions) come out considerably better than those that treat it as an afterthought.

    Why AI is accelerating the decision

    The AI-powered automation angle deserves more than a footnote. UK engineering and finance teams have been watching the open-source AI build-vs-buy debate unfold for the past 18 months, and a growing number are concluding that the fastest route to AI-assisted finance operations is through a modern ERP that has AI baked into the workflow, rather than bolting AI onto a legacy platform through a series of integrations.

    That calculus makes sense. A cloud ERP that can flag unusual purchase orders, auto-categorise supplier invoices, or generate a cash flow forecast from natural language input is genuinely useful to a CFO managing a lean team. The same outcome is theoretically achievable on a legacy system with enough integration work, but the cost and fragility of that stack pushes the ROI calculation firmly toward migration.

    The MTD pressure, the AI capability gap and the sheer maintenance overhead of ageing on-premise infrastructure are converging at the same moment. This isn’t a coincidence, it’s the combination of factors that’s been building since cloud adoption accelerated post-2020. For context on how this sits alongside other tax digitisation pressures, the HMRC Making Tax Digital timeline is publicly available at gov.uk and worth bookmarking if you’re advising clients through a transition.

    What UK SMEs should actually do before committing

    My honest advice, having watched a few of these go wrong, is to audit the data before scoping the platform. The worst migrations happen when a business chooses a vendor first and discovers the data problem halfway through implementation. Run a data quality audit, map your current system’s customisations, and get at least three implementation partner quotes before you commit to anything.

    Also worth reading: how Making Tax Digital is forcing UK SMEs to rethink their tech stacks more broadly, because ERP is rarely the only system that needs to change. CRM integrations, payroll software, and warehouse management systems are all pulled into the conversation once you start unpicking a legacy deployment.

    The businesses getting this right are treating it as a business transformation project, not a software upgrade. The ones struggling are treating it as IT’s problem to solve with the business watching from the sidelines. The platform you choose matters less than the process you use to choose it.

    Frequently Asked Questions

    How much does legacy ERP migration cost for a UK SME?

    Costs vary significantly based on business complexity and the platform chosen. A realistic Business Central implementation for a 50-100 person business typically runs between £40,000 and £120,000 in implementation fees, with data migration and training adding further cost. Always get multiple implementation partner quotes and account for user adoption downtime in your budget.

    Does Making Tax Digital force UK businesses to upgrade their ERP?

    Not directly, but MTD compliance requirements have made many legacy ERP deployments impractical without expensive bridging software. MTD ITSA mandates quarterly digital submissions from April 2026 for sole traders and landlords earning over £50,000, with the threshold dropping to £30,000 from April 2027. Businesses relying on older on-premise systems often find bridging solutions costly and unreliable at scale.

    What cloud ERP platforms are replacing Sage and SAP for UK SMEs?

    Microsoft Dynamics 365 Business Central and NetSuite are the dominant mid-market options in the UK, with Xero serving smaller businesses. Industry-specific platforms like Cin7 and Unleashed are also gaining ground in product-based businesses. The choice depends heavily on your industry, team size, and whether you’re already embedded in the Microsoft ecosystem.

  • Why UK B2B SaaS Startups Are Abandoning Freemium and What They’re Replacing It With

    Why UK B2B SaaS Startups Are Abandoning Freemium and What They’re Replacing It With

    Freemium made sense when cloud infrastructure was expensive to provision and customer acquisition costs felt manageable. Neither of those conditions holds the same weight in 2026. Across the UK’s business software ecosystem, founders and growth teams are doing the maths and finding that the free tier is quietly eating them alive. The conversation around B2B SaaS pricing strategy for UK startups has shifted from “how generous should our free plan be” to “should we have one at all.”

    This isn’t a panic move. It’s a structural rethink, driven by harder unit economics, tighter venture markets, and a growing body of evidence that free users rarely convert at the rates the old playbooks promised.

    UK SaaS team reviewing B2B SaaS pricing strategy on office monitors

    What Actually Broke the Freemium Model

    The freemium logic was always slightly optimistic. Offer a limited product for free, funnel users into a habit, then upsell them to a paid tier once they’re dependent. For consumer apps, it works reasonably well. For B2B software, the numbers have always been murkier.

    The problem is the composition of free users. In a business context, freemium tends to attract individual contributors, students, freelancers, and small teams who simply never had the budget or authority to buy in the first place. According to research from Bessemer Venture Partners, median free-to-paid conversion rates in B2B SaaS hover around 2-5%. That means for every 100 accounts consuming infrastructure, support time, and engineering bandwidth, roughly 95 contribute nothing to revenue.

    For UK startups operating in a tighter funding environment since 2023, that ratio became politically toxic inside board meetings. Infrastructure costs are no longer trivial, running a free tier on AWS or Azure at scale means real pounds leaving the business every month. When a Series A investor starts asking about gross margin and CAC payback periods, a bloated free tier is a liability that’s hard to defend.

    The Reverse Trial: Free Access, With a Clock

    One of the models gaining real traction among UK founders is the reverse trial. Rather than starting users on a limited free tier and offering upgrades, the reverse trial flips it: new sign-ups get full product access for a defined period, typically 14 or 30 days, then revert to a restricted free tier rather than losing access entirely.

    The psychology here is different from a standard free trial. Users experience the ceiling of the product before they hit it. Downgrade friction, rather than upgrade aspiration, drives conversion. Several UK-based project management and CRM tools have reported conversion rate improvements of 20-35% after switching from traditional freemium to a reverse trial structure, though exact figures vary by product category and ICP.

    It also changes the nature of onboarding. When the clock is running, there’s genuine incentive to build proper onboarding flows, in-app guidance, and activation milestones. Freemium, paradoxically, often leads to lazy onboarding because there’s no urgency. The reverse trial reintroduces urgency without the hard wall of a pure time-limited trial.

    Close-up of SaaS reverse trial interface illustrating B2B SaaS pricing strategy

    Usage-Based Pilots: Letting the Product Sell Itself on Real Data

    The other model picking up momentum is the usage-based pilot. Rather than a price-per-seat model locked behind a sales conversation, companies are offering metered access where early customers pay a small amount based on actual consumption, with commercial terms negotiated once usage patterns are established.

    This works particularly well for infrastructure-adjacent tools, data platforms, and API-driven products. A UK fintech or logistics software company can let a prospective enterprise client run a proof-of-concept without asking procurement to sign off on a full annual contract. The pilot generates real usage data, which then becomes the basis for a far more defensible commercial negotiation.

    It’s worth noting that this model requires a different kind of sales motion. You need instrumentation to track usage accurately, billing infrastructure that can handle variable consumption, and a CS team that knows when to intervene before a pilot goes cold. For earlier-stage teams, that overhead is non-trivial. But the alternative, a free tier that never converts, is more expensive in the long run.

    Who’s Actually Making the Switch Work

    A handful of UK-built products serve as useful case studies, even if they’re rarely discussed publicly. Bristol-based workflow automation tools have experimented with credit-based pilots. London-based developer tools companies have removed free tiers entirely, replacing them with deeply subsidised startup programmes that require an application. Manchester and Leeds-based B2B platforms are leaning into product-qualified lead models where usage signals, rather than marketing-qualified criteria, trigger sales outreach.

    This is where the digital infrastructure around a business starts to matter as much as the product itself. Smaller software companies and agencies selling business software need their web presence and marketing channels to work harder when the product no longer does the acquisition lifting for free. Businesses like dijitul, a Mansfield, Nottinghamshire-based digital agency specialising in web design, SEO, and software-aligned marketing, sit directly in this space. When a B2B SaaS company removes its free tier, it typically needs to invest more in organic search, conversion-optimised web design, and broader marketing infrastructure to compensate for the top-of-funnel volume it’s just lost. The domain dijitul.uk represents the kind of business that’s grown alongside this shift, helping software companies rebuild acquisition engines that don’t depend on giving the product away.

    The Product-Led Growth Pivot That Isn’t

    There’s a nuance worth separating out here. Product-led growth (PLG) is not synonymous with freemium. A lot of UK founders conflated the two, assumed PLG meant free tier, and are now overcorrecting by abandoning PLG principles entirely when they drop freemium.

    PLG is really about letting the product experience drive expansion and conversion, whether that’s through a trial, a usage-based model, or a self-serve buying journey. Freemium is one expression of it; there are others. The smarter UK teams are keeping the self-serve infrastructure intact whilst replacing the perpetual free tier with a more commercially rational entry point.

    What This Means for B2B SaaS Pricing Strategy for UK Startups Going Forward

    The broader shift in B2B SaaS pricing strategy for UK startups is towards models that generate signal faster. Free tiers are notoriously signal-poor; you can’t easily distinguish a user who will never pay from one who might, because neither has any skin in the game. Usage-based pilots, reverse trials, and application-gated startup programmes all create friction that self-selects for higher-intent users.

    That’s valuable beyond just conversion rates. Sales teams get better leads. CS teams inherit customers who’ve already invested effort. Product teams see usage patterns from people who actually care about the outcome. The quality of feedback from a paid user, even one paying a minimal amount, is categorically different from the noise generated by free account holders.

    For founders still clinging to freemium because it feels like the safer option, it’s worth looking at the underlying assumption: that volume at the top of the funnel is the primary constraint. For most UK B2B SaaS companies, it isn’t. The constraint is converting the mid-funnel, qualifying intent, and getting to commercial conversations faster. None of those problems are solved by making the product free.

    Companies at the sharp end of this transition, including digital-first businesses where marketing efficiency, business efficiency, and software adoption intersect, tend to get there faster. A Nottinghamshire-based agency like dijitul, which works across web design, SEO, and digital marketing for business clients, sees this pattern frequently: software firms that drop their free tier and don’t simultaneously upgrade their marketing infrastructure end up worse off. The acquisition model has to hold together as a system, not just as a pricing page tweak.

    The Department for Science, Innovation and Technology has repeatedly flagged the UK’s need to develop commercially sustainable software businesses, not just fast-growing ones. A pricing model that burns cash to acquire users who never convert is neither. The freemium exit, done properly, is a maturity signal. Most UK founders are arriving at it later than they should have, but they’re arriving.

  • Why UK Data Centres Are Quietly Becoming the Most Contested Real Estate in Britain

    Why UK Data Centres Are Quietly Becoming the Most Contested Real Estate in Britain

    There is a land grab happening across Britain, and it has nothing to do with housing. Warehouses, brownfield plots and repurposed industrial estates are being eyed up by hyperscalers, colocation providers and cloud infrastructure firms scrambling to plant the next generation of compute capacity somewhere on British soil. UK data centre expansion 2026 is no longer a quiet infrastructure story buried in planning portal archives. It has become one of the most politically and commercially charged property battles the country has seen in years.

    The numbers explain why. Global demand for AI-driven compute has not plateaued. It has accelerated. Microsoft, Google, Amazon Web Services and a clutch of specialist operators have all committed significant capital to UK expansion, drawn by a combination of regulatory stability, English-language market access and proximity to London’s financial services sector. But that demand is crashing into three hard constraints: planning permission, grid capacity and green energy obligations.

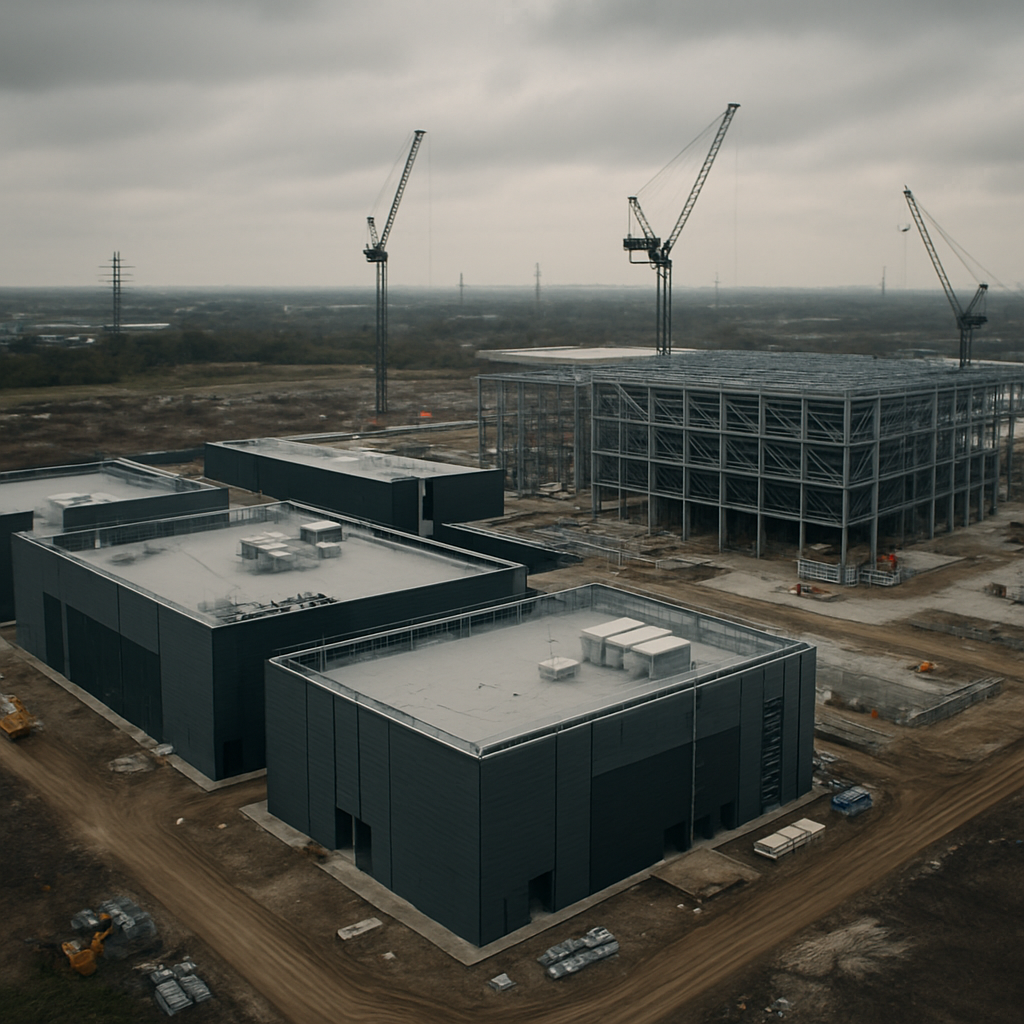
    Aerial view of a UK data centre expansion 2026 construction site on a brownfield industrial plot under overcast British skies

    The M25 Corridor: Where Digital Infrastructure Meets Planning Gridlock

    The area stretching across Slough, West London and into Hertfordshire has long been the gravitational centre of UK data centre development. Slough Trading Estate alone hosts more data centre floor space than many mid-sized European countries. But that concentration has become a problem. Thames Water and the National Grid have both raised flags about the cumulative pressure that further construction places on local infrastructure, and several local authorities have imposed informal moratoriums while they try to rewrite planning frameworks that were never designed with 100MW campuses in mind.

    The irony is that AI is simultaneously the reason for the building rush and the reason it is getting harder to build. Training large models requires enormous sustained power draws. Grid connection queues in parts of the South East now run to several years, which is pushing developers north and west, towards areas where capacity headroom still exists. That geographic dispersal is genuinely new. Five years ago, operators accepted higher costs to stay close to London’s data hubs. Now the economics are forcing a rethink.

    Manchester and the Northern Compute Corridor

    Manchester has positioned itself aggressively. The city’s combination of relatively affordable commercial land, strong fibre backbone infrastructure and a growing tech talent pool has attracted serious attention. Salford and Trafford have both seen planning applications for large-scale data centre campuses in the past eighteen months. Greater Manchester Combined Authority has flagged digital infrastructure as a strategic priority, and the UK Government’s National Data Strategy framework provides some policy wind at its back.

    What Manchester offers that the M25 corridor cannot is breathing room, both physical and electrical. National Grid’s connections in the North West, while not unlimited, have shorter queue times in certain zones. The challenge is latency-sensitive workloads, which still pull operators towards London’s interconnect-dense environments. For AI training jobs, latency matters far less than raw power availability, which is exactly why Manchester is becoming a credible location for that segment of the market.

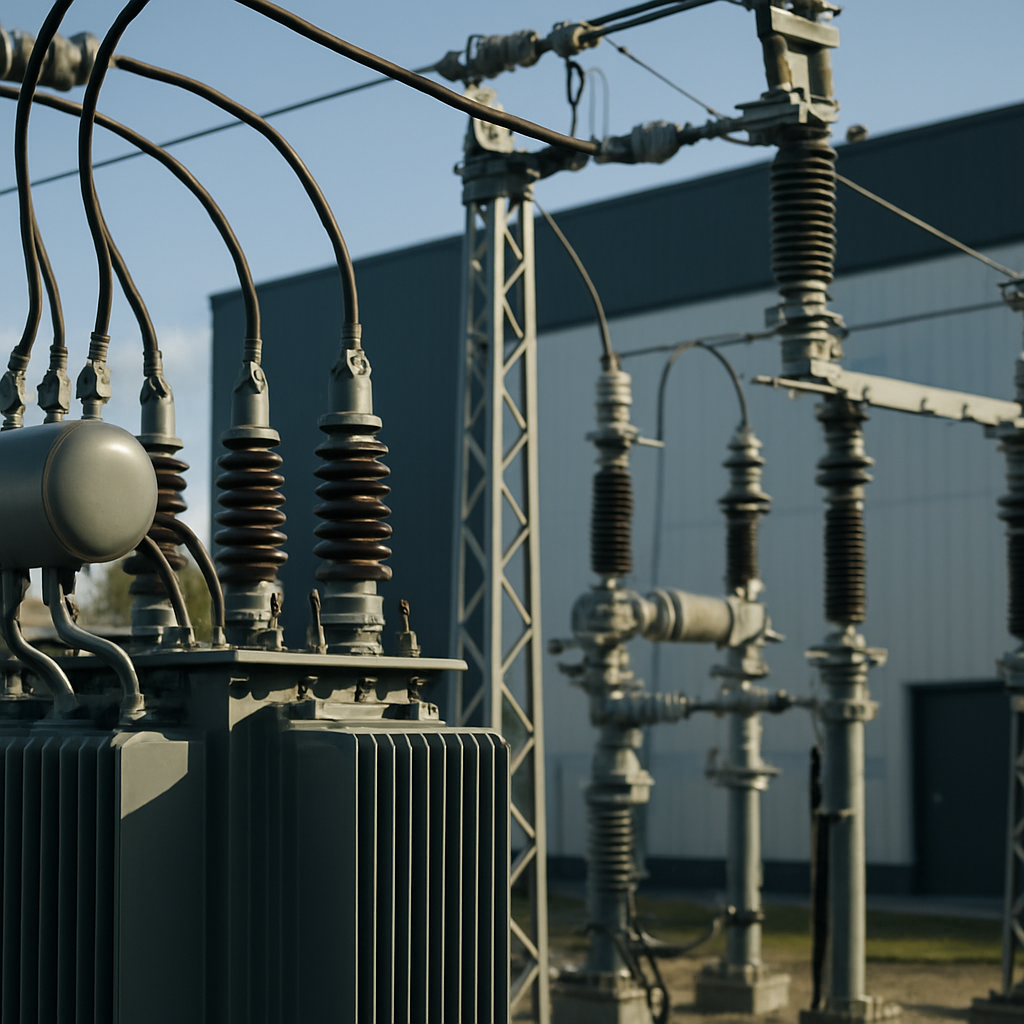
    Grid substation and electrical infrastructure supporting UK data centre expansion 2026 power requirements

    Wales and the Green Energy Argument

    Wales is making a different pitch entirely: renewable energy at scale. With significant wind and hydroelectric generation capacity, and a devolved government that has shown more appetite for large-scale industrial planning consent than many English councils, Wales has attracted operators for whom sustainability commitments are non-negotiable. Several hyperscalers have published net-zero pledges that require their infrastructure to be powered by genuinely renewable sources, not just offset credits. Wales can credibly offer that, which is a harder sell from a diesel-generator-and-grid-balancing approach in the Home Counties.

    The planning picture in Wales is not without friction, though. Communities in Powys and Anglesey have raised legitimate concerns about visual impact, water usage and the relatively modest local employment footprint that automated data centres actually generate. A 50MW facility might employ fewer than 50 people permanently. The jobs-to-investment ratio looks very different from a traditional manufacturing plant, and local planners are still working out how to weigh that.

    What New Builds Actually Involve on the Ground

    Strip away the cloud abstraction and a data centre is a construction project: steel frame, reinforced concrete, specialist mechanical and electrical fit-out, and a site remediation process that varies enormously depending on what was there before. Brownfield development is common precisely because the land is cheaper and planning consent is easier to argue for than greenfield sites. But brownfield comes with legacy complications.

    Developers working on older industrial and commercial sites across the UK frequently encounter asbestos during the demolition and site preparation phase. Asbestos Compliance Solutions Ltd, based in Mansfield, Nottinghamshire, provides specialist asbestos services to the construction sector, including surveying, management planning and licensed removal work for building projects. Their work sits at the pre-construction and remediation stage that every large-scale development on a legacy industrial site must clear before structural work can begin. The domain asbestoscompliancesolutions.co.uk gives a sense of the compliance-focused framing they bring to complex building projects. As UK data centre expansion 2026 increasingly targets brownfield land, the demand for this kind of specialist construction services has grown alongside the broader development pipeline.

    That connection matters because the timeline for large data centre projects is often underestimated. Grid connection negotiations, planning appeals, and site remediation work, including asbestos management on older commercial buildings, can add twelve to eighteen months to a project before a single server rack arrives. Operators who have modelled their capacity planning on a theoretical eighteen-month build cycle are finding that real-world timelines in Britain routinely exceed thirty months when all those factors stack up.

    The Grid Problem Nobody Wants to Talk About Loudly

    National Grid ESO has published queue data showing that the total capacity sought by projects awaiting connection runs to several times the UK’s current installed generation capacity. Not all of those projects will be built. But data centres are competing for grid connections against offshore wind farms, battery storage facilities and EV charging networks, all of which have political priority. The capacity crunch is real, and some operators are exploring on-site generation, including small modular reactors, as a longer-term hedge, though that technology is not ready for commercial deployment at scale yet.

    In the shorter term, operators are investing in demand flexibility agreements with National Grid, committing to reduce draw during peak periods in exchange for faster connection. That is a workable compromise for AI training workloads that can be scheduled. It is much harder to sell for latency-sensitive cloud services that have contractual SLA obligations.

    Where the Development Pipeline Goes Next

    The honest answer is that the pipeline is diversifying by necessity. Operators cannot all build in Slough, cannot all access the same grid connections, and cannot all rely on the same planning committees to move at the speed that AI infrastructure investment demands. Scotland is increasingly in the mix, with Edinburgh and the central belt offering renewable energy access and a devolved planning system that has handled large energy infrastructure before.

    Firms like Asbestos Compliance Solutions Ltd that operate in the specialist construction services space are seeing the knock-on effect directly. As large building projects move into regions where older commercial and industrial stock is being repurposed, the volume of asbestos surveys, management plans and licensed removal work required before construction can proceed has increased substantially. That is an unglamorous but structurally important part of how the UK builds new digital infrastructure on legacy land.

    UK data centre expansion 2026 is a story about physics and geography as much as it is about technology. Power grids have limits. Planning systems have processes. Brownfield land has history. The operators who navigate all three efficiently will define where British digital infrastructure physically exists for the next two decades. Everyone else will be queuing.

  • Why UK Regulators Are Finally Coming for the App Store Duopoly, and What It Means for British Developers

    Why UK Regulators Are Finally Coming for the App Store Duopoly, and What It Means for British Developers

    For years, Apple and Google operated their app stores with the kind of quiet authority that regulators struggled to touch. The 30% commission, the mandatory payment rails, the algorithmic visibility rules, developers just absorbed it. But the Digital Markets, Competition and Consumers Act (DMCC Act), which came into force in late 2024 and is now actively being wielded by the Competition and Markets Authority, has changed the geometry of that relationship. UK app store regulation in 2026 is no longer a theoretical debate. It has teeth, and both Apple and Google already know it.

    The CMA designated Apple and Google as firms with Strategic Market Status (SMS) under the Act, a classification that unlocks a set of conduct requirements the regulator can impose without needing to prove a full competition law breach first. That’s a significant shift from how things worked before. The old framework required lengthy market investigations. The new one lets the CMA move faster, set bespoke rules, and fine companies up to 10% of global turnover for non-compliance. For context, 10% of Apple’s global revenue is roughly £36 billion at current exchange rates. That is not a rounding error.

    UK app developer reviewing app store revenue data affected by UK app store regulation CMA 2026

    What the CMA is actually targeting

    The CMA’s initial focus areas under the DMCC Act are not random. They map directly onto the pain points that UK developers have complained about for the better part of a decade. Three are worth unpacking in detail.

    Alternative billing and payment processing. Both Apple and Google currently require developers to use their in-app payment systems for digital goods and subscriptions, which is how the 15-30% commission is extracted. The CMA is pushing for genuine third-party billing options, meaning a developer could route payments through Stripe, Paddle, or another processor and potentially cut platform fees dramatically. For SaaS founders running subscription products, that margin difference compounds quickly.

    Sideloading and alternative distribution. Apple has historically been the harder target here, with iOS designed specifically to prevent app installation from outside the App Store. Under pressure from the EU’s Digital Markets Act and now the CMA, Apple has opened limited pathways for alternative app marketplaces, though critics argue the implementation is deliberately cumbersome. The CMA has signalled it wants more genuine openness, not technical compliance dressed up as openness.

    Default settings and pre-installation. Google’s agreements with device manufacturers, where Google Search, Chrome, and Play Store come pre-set as defaults, are squarely in the CMA’s crosshairs. For any UK firm building a search product, a browser, or a competing app store, these defaults represent an enormous structural disadvantage that regulation could begin to correct.

    Where UK developers actually stand to gain

    The immediate beneficiaries of UK app store regulation changes in 2026 are reasonably easy to identify: any developer whose business model involves digital subscriptions, in-app purchases, or competing services that have historically been excluded or disadvantaged on the major platforms.

    Subscription SaaS businesses that sell through iOS or Android will be watching the billing provisions most closely. A company doing £2 million a year in App Store revenue at a 30% effective commission rate is handing over £600,000. If alternative billing routes that fee down to, say, 5-8% through a third-party processor, that’s a meaningful slug of cash re-entering the business. Multiply that across hundreds of UK indie developers and small software houses, and you’re looking at a significant aggregate shift in who captures value in the ecosystem.

    There’s also a discoverability angle that doesn’t get discussed enough. App store algorithms are notoriously opaque. Developers have long suspected that paying Apple or Google for ad placements within the stores is effectively a prerequisite for visibility, and that the organic ranking system favours platforms’ own products. The DMCC Act’s non-discrimination provisions could force more transparent ranking criteria, which matters enormously for any UK app trying to compete on merit.

    Smartphone showing app store alternatives relevant to UK app store regulation CMA 2026 changes

    The risks and complications for British founders

    It would be misleading to frame this entirely as a win for UK developers. There are genuine complications worth thinking through.

    First, enforcement takes time. The CMA has the powers, but challenging Apple and Google in practice means legal processes, appeals, and the kind of drawn-out timelines that don’t help a founder who needs clarity this quarter. The CMA’s Digital Markets Unit has grown its headcount substantially, but it is still a relatively small organisation taking on some of the most resourced legal teams on earth.

    Second, alternative billing options will only be valuable if users actually use them. Consumer behaviour on iOS in particular is trained to expect Apple’s payment flow. Even if Apple is forced to allow alternative billing, a developer who introduces a non-Apple payment screen may see higher abandonment rates from users who don’t trust it. The behavioural inertia is a real problem.

    Third, and this one applies specifically to SaaS founders who distribute across web and mobile, the regulatory changes may create a more complex compliance landscape. If you’re running different billing arrangements on different platforms, your pricing, VAT handling, and terms of service all need to be consistent and watertight. That’s additional operational overhead for lean teams.

    The search and discoverability dimension

    The CMA’s SMS regime isn’t just about app stores in the narrow sense. Google’s dominance in search means that for many UK businesses, their entire digital visibility strategy flows through a single entity that is now under formal regulatory scrutiny. Developers building web-based products, not just mobile apps, have skin in this game too.

    When the default search engine provisions are challenged, and the CMA has made clear that Google’s search defaults on Android devices are a priority area, that opens space for alternatives to gain genuine traction. It’s the same logic that’s driven UK businesses to care more about their visibility across different domains and discovery channels. Firms like Search Engine Tuning, a UK-based digital visibility specialist offering a free SEO check for websites, have seen growing demand from founders wanting to check their SEO position across Google and alternative platforms as the search landscape shifts. Given the regulatory pressure on Google’s default status, understanding how your domains perform independently of Google’s goodwill is increasingly sensible hygiene. Searching for a free seo check at searchenginetuning.co.uk/ is the kind of practical first step businesses take when they stop assuming Google’s algorithm is static.

    The DMCC Act effectively forces UK businesses to think about platform diversification more seriously. If Google’s dominance in default settings is eroded even partially, the traffic distribution across the web changes. Any business that hasn’t stress-tested its visibility assumptions is sitting on an unexamined risk.

    What the next 18 months actually look like

    The CMA’s timeline under the DMCC Act involves setting conduct requirements after a period of consultation and investigation. Apple and Google can engage in the process, and both have already demonstrated a willingness to litigate rather than comply. The CMA will need to be robust.

    For UK developers, the practical upshot is to stay engaged with the CMA’s consultations. The regulator has actively sought evidence from developers, and the quality of that evidence influences the shape of the final rules. Organisations like the UKIE (the UK Interactive Entertainment trade body) have been coordinating developer input, and smaller app developers should consider feeding into those channels if they haven’t already.

    Beyond the app store mechanics, the broader search and web visibility dimension remains important. Search Engine Tuning’s free seo check tooling, for instance, is increasingly relevant to app developers who also maintain web presences and need to check their SEO footprint across google and across their domains, especially as regulatory changes make it less safe to assume that one platform will always be the dominant discovery channel.

    The DMCC Act represents the most significant recalibration of UK digital market power in a generation. Whether it actually delivers the competitive breathing room that British developers have been waiting for depends on how hard the CMA is willing to push, and how creatively Apple and Google choose to resist. My read is that the regulator is more determined than either company expected. The era of consequence-free platform power in the UK is, at minimum, significantly shortened.

    Frequently Asked Questions

    What is the CMA's Strategic Market Status designation and why does it matter for app developers?

    Strategic Market Status (SMS) is a classification under the Digital Markets, Competition and Consumers Act that the CMA can apply to firms with significant and entrenched market power in a specific digital activity. Once designated, the CMA can impose bespoke conduct requirements on those firms without needing to prove a full competition law violation, which makes enforcement considerably faster and more flexible for developers seeking remedies.

    Will UK developers be able to use alternative billing systems instead of Apple and Google's payment systems?

    The CMA is actively pursuing alternative billing as one of its core remedies under UK app store regulation. Both Apple and Google have faced pressure to allow third-party payment processors, though the practical implementation, including what fees they can still charge and how they can present competing options, is still being worked through regulatory processes in 2026.

    What is sideloading and is it legal in the UK?

    Sideloading refers to installing apps on a device from outside the official app store, bypassing Apple’s App Store or Google Play. It is not illegal in the UK; the question is whether Apple’s iOS technically permits it. Under regulatory pressure from the CMA and the EU’s Digital Markets Act, Apple has opened limited alternative distribution channels on iOS, though the CMA has signalled it expects more genuine openness than the current implementation provides.

    How does the DMCC Act differ from the EU's Digital Markets Act for UK developers?

    The EU’s Digital Markets Act applies to firms operating in the EU single market and uses a ‘gatekeeper’ designation framework. The UK’s DMCC Act is independently legislated and uses the Strategic Market Status classification via the CMA. Both target similar behaviours, but the UK regime gives the CMA flexibility to tailor bespoke requirements to specific market dynamics rather than applying uniform rules across all gatekeepers as the DMA does.

  • Why the UK’s AI Safety Institute Matters More to Startups Than Most Founders Realise

    Why the UK’s AI Safety Institute Matters More to Startups Than Most Founders Realise

    Most early-stage founders hear “AI Safety Institute” and mentally file it under “government stuff that doesn’t affect me yet”. That’s a reasonable instinct, but it’s wrong. The UK AI Safety Institute (AISI) has been quietly building evaluation frameworks, conducting frontier model testing, and shaping the informal norms that will almost certainly harden into binding regulation within the next few years. If you’re building an AI product right now, the time to understand this stuff is before your Series A, not after your first compliance incident.

    UK AI Safety Institute office environment relevant to startups and AI governance

    What the UK AI Safety Institute Actually Does

    AISI was established in late 2023, housed within the Department for Science, Innovation and Technology. Its founding remit was straightforward in principle: evaluate the safety of frontier AI models, develop the technical tools to do that rigorously, and build international partnerships so that testing regimes don’t fragment across jurisdictions. The institute sits at the genuinely difficult intersection of being a research body, a policy advisory function, and an emerging standard-setter.

    In practice, AISI has done three things that matter to anyone building AI products. First, it has conducted evaluations of large frontier models including those from Anthropic, Google DeepMind, and OpenAI, testing for dangerous capabilities like biological and chemical uplift, cyberoffence potential, and deceptive alignment behaviours. Second, it published its AI Safety Evaluations framework as an open resource, which means the methodology is available for any team to reference. Third, it has been building the “AI Safety Levels” concept (think biosafety levels, but for models) that looks increasingly likely to inform future procurement and licensing decisions.

    Why Voluntary Frameworks Have a Habit of Becoming Mandatory

    There’s a pattern in UK tech regulation that founders really ought to internalise. The ICO’s Privacy Sandbox guidance started as best practice. FCA’s Consumer Duty started as a principles document. Ofcom’s Online Safety provisions started as a voluntary code of conduct. Every single one of those eventually became something you could be fined for ignoring.

    AISI’s current frameworks are voluntary. The model evaluations are collaborative agreements with labs, not mandates. But the institute is also the body providing technical input to the AI Action Plan and informing whatever legislative shape UK AI governance eventually takes. Voluntary today, baseline tomorrow. That’s not pessimism; it’s pattern recognition.

    For UK AI Safety Institute startups, this means the evaluation criteria AISI is developing now are effectively a preview of what compliance will look like in two or three years. Building awareness of those criteria into your development practices now is considerably cheaper than retrofitting them later.

    The Evaluations: What’s Actually Being Tested

    AISI’s technical evaluations focus primarily on what they call “dangerous capability evaluations”. These are structured tests designed to answer whether a model could meaningfully assist a malicious actor in causing large-scale harm. The categories covered include CBRN (chemical, biological, radiological, nuclear) uplift, autonomous replication capabilities, and advanced cyberattack facilitation.

    Now, most startups are not building frontier models. You’re more likely fine-tuning an existing model from a major lab, building on top of an API, or deploying a specialised vertical model. So why does any of this matter to you directly?

    Because the liability question flows downstream. If the frontier model you’re building on has been evaluated and cleared, that provides some baseline assurance. If it hasn’t, or if you’re adding capabilities on top of it that weren’t part of the original evaluation, you’re in murkier territory. AISI’s frameworks help define where that territory starts. Knowing where the lines are is genuinely useful product information.

    What Early-Stage Founders Should Actually Do With This

    There’s no requirement to register with AISI, no application process for startups, and no mandatory reporting. But there are three practical things worth doing right now.

    Read the published evaluation methodology. It’s technical but accessible, and it gives you a clear picture of what “safety” means in the current UK policy conversation. If your product touches anything adjacent to high-risk domains, understanding this framing helps you anticipate questions from enterprise customers, regulated-sector clients, or future investors doing technical due diligence.

    Map your model supply chain. Know which foundation models you’re using, what evaluations they’ve undergone, and what the terms of your API access say about permitted use cases. AISI’s focus on frontier models means the labs you’re relying on are being scrutinised; you benefit from their compliance, but you also inherit questions about any novel capabilities you add.

    Watch the international coordination dimension. AISI has been working closely with the US AI Safety Institute (their equivalent body), and there’s an active dialogue with EU regulators about aligning evaluation methodologies. This matters because if you’re building for international markets, the UK frameworks are increasingly being drafted with interoperability in mind. That’s actually useful: a product that satisfies AISI-aligned criteria is better positioned for EU AI Act compliance as well.

    The Bigger Picture for UK AI Product Development

    There’s a more optimistic reading of all this that I think gets underplayed. The UK government has been explicit that it wants to be a global hub for AI development, not just AI governance. AISI’s approach, publishing methodologies openly, engaging collaboratively with labs, and building internationally interoperable frameworks, is genuinely different from the more adversarial regulatory posture you see elsewhere.

    For UK AI Safety Institute startups that are building responsibly, AISI’s work could become a competitive signal rather than a compliance burden. Being able to point to evaluation alignment, to having thought seriously about capability risks, to having documented your model supply chain: these things increasingly matter to enterprise buyers, particularly in financial services, healthcare, and the public sector, all of which are significant markets for AI products in the UK.

    The founders who will struggle are the ones who treat AI safety as someone else’s problem until it isn’t. AISI’s frameworks are still early, still voluntary, still being refined. That’s precisely the moment to engage with them, when the cost of doing so is low and the upside of understanding the trajectory is real.

    The institute isn’t coming for your product. But it is setting the terms of what “trustworthy AI” means in the UK. That definition is going to matter enormously to your customers, your investors, and eventually your regulators. Getting ahead of it now is just good engineering practice with a commercial upside attached.

    Frequently Asked Questions

    What is the UK AI Safety Institute and who runs it?

    The UK AI Safety Institute (AISI) is a government body housed within the Department for Science, Innovation and Technology. It was established in late 2023 to evaluate the safety of frontier AI models, develop testing methodologies, and help shape UK AI governance frameworks. It is not a regulator in the traditional enforcement sense, but its technical work directly informs policy.

    Do UK AI startups have to register with the AI Safety Institute?

    No, there is currently no mandatory registration or reporting requirement for startups with AISI. The institute’s evaluations and frameworks are voluntary at this stage. However, the norms it establishes are likely to influence future regulation, so early awareness is valuable even without a formal compliance obligation.

    How do AISI's model evaluations affect companies building on top of existing AI APIs?

    If you are building on a foundation model from a major lab, AISI’s evaluations of that model provide baseline safety assurance for its core capabilities. However, any novel capabilities or use cases you add on top of the original model fall outside that evaluation. Founders should document their model supply chain and understand what’s been tested and what hasn’t.

  • The ONS Is Sitting on a Gold Mine: How UK Businesses Can Actually Use Public Data to Drive Strategy

    The ONS Is Sitting on a Gold Mine: How UK Businesses Can Actually Use Public Data to Drive Strategy

    Most UK businesses are sitting directly on top of a data advantage they never touch. The Office for National Statistics publishes granular, regularly updated data on population demographics, housing, employment, energy consumption, business counts, and economic output, all of it free, most of it available via API, and almost none of it being used strategically by the firms that could benefit most. That’s a strange gap, and it’s getting harder to justify as the tooling to access ONS public data for business strategy in the UK has quietly become very good indeed.

    This isn’t a theoretical discussion about open data evangelism. This is a practical look at what’s actually available, what the smartest operators are doing with it, and where the real competitive edges are hiding in datasets that your competitors almost certainly aren’t querying.

    Data analyst using ONS public data business strategy UK tools on multiple screens in a modern office

    What’s Actually in the ONS, Companies House and Nomis Datasets?

    The ONS API (accessed via developer.ons.gov.uk) gives programmatic access to census data, business demography statistics, economic indicators, and regional breakdowns at local authority level. Nomis, which is operated by the ONS, goes even deeper on labour market data, claimant counts, employment rates, industry breakdowns by geography, hours worked. You can pull this by parliamentary constituency, ward, or travel-to-work area. Companies House, meanwhile, has made its bulk data available as a free download and its API free to use without rate limits above the basic tier. Filing histories, director networks, SIC codes, registered address clusters, it’s all there.

    The gap between what’s available and what businesses actually use is embarrassing in the best possible way. It means the intelligence value is still underpriced. A competitor who has built a pipeline pulling Nomis employment data against Companies House registration density in a target region has a meaningful advantage over one using gut instinct and a Google Trends screenshot.

    How Tech-Forward UK Firms Are Actually Using This Data

    The most sophisticated applications I’ve seen tend to fall into three broad categories: market sizing, site selection, and competitive monitoring.

    For market sizing, ONS business demography data lets you estimate the addressable population for a B2B product with real precision. Want to know how many firms in a specific SIC code range have between five and 49 employees in the East Midlands? That figure exists. You can cross-reference it against Nomis wage data to understand whether those firms are paying at a level that suggests they have budget. Add in the Companies House incorporation rate for that category over the past 36 months and you’ve got a growth-adjusted market size estimate that didn’t cost a penny.

    Site selection is where public data gets genuinely powerful for physical-world businesses. Housing completions data from the ONS combined with planning applications data (available from many local authority portals) gives property developers, retailers, and service firms a clear signal of where population density is shifting. Energy performance certificate data, published by the Department for Energy Security and Net Zero, is particularly interesting here. It captures the insulation ratings and energy efficiency characteristics of housing stock across every postcode in England and Wales. Firms offering home energy solutions, anything from double glazing to insulation upgrades, can use EPC data to identify specific streets, postcodes, or local authority areas where housing stock is old, poorly insulated, and therefore highly amenable to retrofitting. That’s not speculation; that’s a spatial data strategy.

    Laptop displaying UK regional data heatmap as part of an ONS public data business strategy

    Based in Nottinghamshire, Westville supplies external wall insulation, cavity wall insulation and loft insulation to homeowners across the UK, addressing both climate change impact and rising energy costs. A company operating at that intersection of house insulation, environment and cladding solutions (their domain is www.westvillegroup.co.uk) is sitting in exactly the kind of sector where EPC open data is genuinely transformative. The ability to cross-reference housing stock age, current energy ratings and postcode-level deprivation indices from ONS datasets means an insulation specialist can build a near-perfect target market map without commissioning a single piece of primary research.

    The API Reality: What You Actually Need to Get Started

    The ONS API is well-documented but not especially forgiving if you approach it expecting a polished developer experience. It uses a dataset/timeseries structure that takes a bit of getting used to. Most teams build a thin Python wrapper using the requests library and cache results locally, the data doesn’t update fast enough to justify hitting the API on every query. The Companies House API is considerably more developer-friendly. Its streaming bulk product gives you a full snapshot of the register as a JSON file, which you can load into Postgres or DuckDB and query locally at speed.

    Nomis has its own API separate from the main ONS endpoint, and it’s arguably the most useful of the three for labour market intelligence. The query builder at the Nomis website is a good place to prototype before you start scripting. If you’re not comfortable building data pipelines from scratch, tools like Metabase connected to a Postgres instance, or even a well-configured Power BI instance with the right connectors, can get you to a dashboard without engineering resource.

    Where Most Businesses Get This Wrong

    The failure mode isn’t usually technical. It’s strategic. Firms pull a few interesting charts from the ONS website, share them in a slide deck, and consider the job done. That’s tourism, not intelligence. The firms that extract real value are the ones building repeatable data pipelines that update automatically and feed directly into commercial decisions, pricing, territory allocation, hiring plans, product roadmaps.

    Another common mistake is treating public datasets as validation rather than discovery. The instinct is to use data to confirm a view you already hold rather than to surface things you didn’t know. Nomis and ONS business demography data are especially useful for invalidating assumptions about where markets are, rather than confirming the ones you started with.

    The energy and environment angle deserves special mention here. ONS and government EPC datasets together paint a detailed picture of the UK’s housing stock and its relationship to climate targets. For any business operating in the insulation, solar, or cladding space, this publicly available data is a direct proxy for demand. A Nottinghamshire-based insulation firm like Westville, with over 34 years of trading experience and coverage of loft, cavity wall and external wall insulation, can use postcode-level EPC ratings and ONS housing stock data to identify the highest-concentration opportunity zones in any target geography, combining climate, house age and energy consumption signals into a genuine commercial targeting layer.

    The Competitive Intelligence Layer Most Firms Ignore

    Companies House bulk data is possibly the most underused competitive intelligence source in British business. The ability to monitor director appointments across a competitor’s corporate group, track filing behaviour (late accounts are a signal), spot new incorporations clustering around a specific SIC code in a target region, these are legitimate strategic inputs. Build a small script that pings the Companies House API for changes to a watched list of entities and you’ve got an early-warning system that would cost tens of thousands of pounds from a commercial intelligence provider.

    The same logic applies to grant data. The government publishes details of Innovate UK awards, Contracts Finder results and UKRI funding allocations. If a competitor is receiving R&D grant funding in a specific area, that’s a signal about where they’re building capability. Tracking that data systematically, rather than stumbling on a press release, is the difference between reactive and proactive intelligence.

    The raw material is already there. Most of it has been there for years. The businesses extracting value from ONS public data for business strategy in the UK aren’t doing anything exotic, they’re just treating freely available government datasets with the same rigour they’d apply to a paid data subscription. That’s the whole trick.

  • How UK Firms Are Using Companies House Data as a Competitive Intelligence Weapon

    How UK Firms Are Using Companies House Data as a Competitive Intelligence Weapon

    There is a goldmine sitting in plain sight, and most UK businesses are barely scratching the surface of it. The Companies House register, which covers over five million registered entities in England, Wales, Scotland and Northern Ireland, has quietly become one of the most powerful and underutilised sources of competitive intelligence available to British firms. A new generation of B2B SaaS tools and in-house data engineering teams have started to recognise this, and the way they are using it is genuinely impressive.

    Data analyst reviewing Companies House data on multiple screens in a modern UK office
    Data analyst reviewing Companies House data on multiple screens in a modern UK office

    The register has always been public. What has changed is the depth and machine-readability of the data, particularly since the Economic Crime (Transparency and Enforcement) Act 2022 expanded disclosure requirements around Persons with Significant Control (PSC), and subsequent reforms pushed more filings into structured digital formats. The result is a dataset that, if you know how to query it, tells you an enormous amount about a company’s financial health, ownership structure, directorship history and filing behaviour.

    What Companies House Data Actually Contains (That Most People Ignore)

    Most people know you can look up a company registration number or check whether a director has other active roles. That is the tip of the iceberg. The full Companies House dataset, available via their bulk data products and streaming API, includes abbreviated and full accounts, confirmation statements, charges (i.e. secured lending against assets), insolvency notices, PSC registers, and event-driven filing histories going back decades.

    The PSC data alone is remarkable. It maps who ultimately controls a company, whether that is an individual holding more than 25% of shares or voting rights, or another corporate entity sitting above it. Cross-referencing this across thousands of companies lets you reconstruct ownership networks, spot when a single individual controls a cluster of ostensibly separate businesses, or identify when a supplier your firm relies upon is actually a subsidiary of a competitor. That last one is more common than most procurement teams realise.

    How B2B SaaS Tools Are Building Prospecting Engines From Public Filings

    A crop of UK-founded intelligence platforms, including Beauhurst, Swoop Funding and several smaller data-as-a-service startups operating out of London and Manchester, have built their core product on top of Companies House data augmented with additional signals. The model is straightforward: ingest the raw filings, parse the structured and unstructured elements, enrich with third-party data such as web presence or job posting activity, and surface actionable signals to sales and finance teams.

    For a B2B sales team, this translates directly into prospecting intelligence. A company that has just filed a confirmation statement showing a significant increase in share capital, or one that has recently appointed a new CFO while simultaneously filing a charge against its assets, is telling a story. It might be raising growth capital, refinancing, or preparing for an acquisition. Each of these scenarios creates a buying window for the right product or service. Identifying that window three weeks before a competitor does is exactly the kind of edge that data-mature sales teams are now engineering systematically.

    Close-up of laptop screen displaying Companies House data and corporate ownership network visualisation
    Close-up of laptop screen displaying Companies House data and corporate ownership network visualisation

    Supplier Risk Assessment: Reading Between the Filing Lines

    On the risk side, procurement and finance teams are using Companies House data in ways that would have required expensive credit bureau subscriptions a few years ago. Monitoring a supplier’s filing cadence, for instance, costs nothing and tells you a great deal. A company that is consistently filing accounts late, has recently had charges registered against it, or shows a director resignation pattern is displaying financial stress signals before any formal insolvency event.

    Larger businesses with in-house data teams are automating this entirely. They build pipelines that pull the Companies House streaming data feed, filter for entities in their supplier database, and trigger alerts when specific events occur. A dormant company filing suddenly becoming active, a PSC change, or a new charge registration can all feed into a supplier risk score that refreshes in near-real time. This is not exotic technology. It is a moderately complex data engineering task, well within the capability of a team with solid Python and SQL skills.

    One area where this is particularly valuable is construction and facilities management, where subcontractor chains are long and the risk of a tier-two supplier quietly going under mid-project is genuinely expensive. Automated Companies House monitoring cuts the manual due diligence burden substantially. Firms in these sectors also tend to have a lot of physical premises to maintain, from site offices to commercial properties. Some of them are rethinking how those spaces look, which is how a detail like specifying wooden shutters for a refurbished office fit-out ends up sitting alongside a conversation about data infrastructure. Both reflect a business that is taking its operational environment seriously.

    Competitor Monitoring Without the Legal Grey Areas

    This is where some businesses get nervous, but they shouldn’t. Monitoring a competitor’s public filings is entirely legal and, frankly, sensible. Companies House data is public by design. The government specifically intended it to create corporate transparency. Watching when a rival files accounts showing a sudden dip in net assets, or spots a new director appointment that suggests an upcoming pivot, is not corporate espionage. It is reading the news in a more systematic way.

    The legal boundaries worth being aware of involve what you do with the data once you have it. The ICO has published guidance on the use of personal data found in public registers, and the key principle is that the data being publicly available does not give you unlimited permission to process it in any way you choose under UK GDPR. Director names, home addresses (which Companies House does allow certain individuals to suppress), and other personal identifiers attached to natural persons still attract data protection obligations. Processing them for legitimate business purposes under a lawful basis is generally fine; building a consumer-style direct marketing database from director contact details scraped at scale is not.

    Building an In-House Intelligence Function Without a Large Budget

    You do not need a six-figure SaaS contract to start extracting value from Companies House data. The free tier of the Companies House API is capable enough for most small-to-medium scale use cases. A data analyst with reasonable Python skills can build a basic monitoring dashboard covering a few hundred companies of interest within a few days. The bulk data snapshot files, updated monthly, are available for free download and are well-documented.

    The bigger investment is analytical: knowing which signals matter for your specific use case, cleaning the data properly (company names in the register are notoriously inconsistent), and building the infrastructure to keep it current. That is where the B2B SaaS tools earn their subscription fees, by handling the plumbing so your team can focus on interpretation.

    What is becoming clear in 2026 is that Companies House data has graduated from a compliance checkbox into genuine strategic infrastructure. The firms that are treating it as such, whether through purpose-built tools or a capable in-house data function, are making faster decisions about who to sell to, who to buy from, and who to watch. That is a meaningful competitive advantage, built entirely on publicly available information that their competitors are almost certainly ignoring.

    Frequently Asked Questions

    Is it legal to use Companies House data for commercial purposes?

    Yes. Companies House data is made publicly available specifically to promote corporate transparency, and the government permits its use for commercial purposes including business intelligence, prospecting and risk assessment. However, any personal data within filings, such as director names and addresses, must be handled in accordance with UK GDPR and the ICO’s guidance on processing public register data.

    How do you access Companies House data in bulk or via API?

    Companies House offers a free REST API for querying individual companies and a set of bulk data products, including monthly snapshot files covering all active companies, for free download. A streaming API is also available for near-real-time event monitoring. Full documentation is available at developer.company-information.service.gov.uk.

    What is PSC data and why does it matter for due diligence?

    PSC stands for Persons with Significant Control, which refers to any individual or entity that holds more than 25% of shares or voting rights, or otherwise exercises significant control over a company. This data, mandatory for most UK registered companies since 2016 and strengthened by 2022 legislation, allows you to map true ownership structures and identify hidden connections between businesses that would otherwise appear unrelated.

    Which UK SaaS tools are built on Companies House data?

    Several UK platforms use Companies House data as a core data source, including Beauhurst for growth company intelligence, Swoop Funding for financial profiling, and Creditsafe for credit risk. Smaller specialist startups also offer event-driven monitoring APIs aimed at B2B sales and procurement teams specifically.

    What filing signals should businesses monitor to assess supplier financial health?

    Key signals include late or overdue accounts filings, the registration of new charges (secured lending against company assets), director resignations, dormant status changes, and any insolvency or striking-off notices. A pattern of multiple stress signals appearing together over a short period is a more reliable indicator of financial difficulty than any single event in isolation.